After Microsoft's historic Mega Patch Tuesday, enterprise IT teams worldwide are scrambling as a wave of updates triggers system meltdowns, broken domains, and silent Excel failures. Find out how AI-driven speed collided with real-world chaos.
- Andrew Ng weighs-in on AI Doomsaying.
- The wisdom of outsourcing AI security testing.
- The true risk of an AI-created bioweapon.
- The EU KIDS Act -- this one is even messier.
- "Nightmare Eclipse" finally unmasks himself.
- A whitehat firm used Claude to attack OpenAI.
- Cisco's own massive 77 CVE update.
- What was the fallout from Sept's Patch Tuesday
Show Notes - https://www.grc.com/sn/SN-1097-Notes.pdf
Hosts: Steve Gibson and Leo Laporte
Download or subscribe to Security Now at https://twit.tv/shows/security-now.
You can submit a question to Security Now at the GRC Feedback Page.
For 16kbps versions, transcripts, and notes (including fixes), visit Steve's site: grc.com, also the home of the best disk maintenance and recovery utility ever written Spinrite 6.
Join Club TWiT for Ad-Free Podcasts!
Support what you love and get ad-free audio and video feeds, a members-only Discord, and exclusive content. Join today: https://twit.tv/clubtwit
Sponsors:
[00:00:00] [SPEAKER_00] It's time for Security Now. Steve Gibson is here. Lots to talk about. Amazing problems that cropped up after Microsoft's patch Tuesday. Steve will run through those. We'll also talk a little bit about the AI doomers and why Steve's not at all worried. He also has his thoughts about the EU Kids Act, which I suspect you already know, but you might want to listen. Security Now is coming up next.
[00:00:27] [SPEAKER_00] This episode is brought to you by Trusted Tech. Trusted Tech has reviewed more than $800 million in Microsoft 365 licensing spend and returned over $100 million to client budgets. On average, that's about 12% of every Microsoft 365 dollar going to waste. Licensing waste doesn't stay small either. Left unmanaged, licensing drift grows 3 to 7% a year. And Microsoft's
[00:00:57] [SPEAKER_00] newer contracts can lock you in for years. Trusted Tech's free Microsoft 365 licensing consultation shows you exactly where you're overspending and how to fix it before your next renewal locks it in. It's not just numbers on a page. Senske Services runs pest control and lawn care crews across the country. After a Trusted Tech review, they unified 1400 devices,
[00:01:21] [SPEAKER_00] right-sized 13% of their Microsoft 365 seats, right-sized 13% of their Microsoft 365 seats, and uncovered more than a thousand licenses they didn't even know they were paying for. Director of Corporate IT, John Christ says, switching to Trusted Tech, let them optimize their licensing and save hundreds of thousands of dollars. And Trusted Tech doesn't stop at the cloud. Why pay Microsoft a percentage of your spend for support?
[00:01:46] [SPEAKER_00] Trusted Tech's certified support starts at $3,000 a year, responds in five minutes, and resolves 85% of tickets in-house, saving up to 52% versus Microsoft unified support. The team also runs deep tenant assignments, handles on-premises Microsoft licensing, and offers Azure cloud consulting to cut infrastructure costs. Licensing, support, on-prem or Azure. Trusted Tech does it all when it comes to Microsoft.
[00:02:15] [SPEAKER_00] Avoid the licensing drift. Go to TrustedTech.team.com right now, submit the form, and lock in your free Microsoft 365 licensing consultation before your next renewal costs you more. TrustedTech.team.com. That's TrustedTech.team.com. Podcasts you love.
[00:02:40] [SPEAKER_01] From people you trust.
[00:02:43] [SPEAKER_00] This is Twit. This is Security Now with Steve Gibson. Episode 1097, recorded Tuesday, September 22nd, 2026. Mega Patch Tuesday fallout. It's time for Security Now. Yay! Tuesday is here, and so is Mr. Steve Tiberius Gibson.
[00:03:08] [SPEAKER_00] Do you think when you're 95, Steve, you'll be doing heavy metal concerts like William Shatner is doing now? He is amazing. He's wild.
[00:03:18] [SPEAKER_01] He is. I just think it's great. And I love that when someone says, what is your secret to longevity? Like, what can you tell us? And he said, don't die.
[00:03:31] [SPEAKER_00] Yeah, that's the best advice ever. Steve, what are we covering on today's mega episode? So, yes.
[00:03:43] [SPEAKER_01] For Security Now 1097. This is the penultimate September episode.
[00:03:51] [SPEAKER_00] He just likes to use that word, kid. So now I know what it means.
[00:03:55] [SPEAKER_01] I want to spend some time talking about the consequences of Microsoft's mega patch Tuesday. We touched on last week. Oh, well, they broke copy and paste for Excel, which you didn't think was a big deal. Of course, all the people whose work day is Excel spreadsheets, they were quite discomfited by that.
[00:04:22] [SPEAKER_01] Turns out that wasn't even the tip of the iceberg of what happened. So it's interesting that on, you know, the good news is that nearly a thousand big problems. There were what, 119 or 117 critical problems solved a couple of weeks ago. Those are gone from Windows. Turns out, though, that there was some fallout from all of that, which we're going to talk about.
[00:04:49] [SPEAKER_01] But first, I wanted to pull in some expert opinion about all of this AI doomsdaying. Andrew Ng weighed in just a couple of days ago. Of course, he's somebody who knows something about AI. I want to share his thoughts about that.
[00:05:09] [SPEAKER_01] Also, he referred to an individual who actually knows something about the bio risks of AI. So we're going to hear from somebody who's actually been there, who is actually both an AI expert and somebody who's made viruses. So is able to cross over as one would have to.
[00:05:34] [SPEAKER_01] Also, you and I were talking about this before, but it's very interesting that all of these breakouts had a single locus that nobody else. I haven't seen anybody else in the industry talk about this.
[00:05:52] [SPEAKER_00] I mentioned it on Sunday, I'm proud to say.
[00:05:54] [SPEAKER_01] Good, because we're going to talk about what I call the wisdom of outsourcing AI security testing. I bet everyone's going to stop that in the future. Also, we've got the EU trying to push their kids act. And boy, this one is even messier than the things they've tried before. Nightmare Eclipse has finally unmasked himself.
[00:06:20] [SPEAKER_01] We know the backstory behind that, which we'll take a look at. Also, a white hat firm, a security firm, used Claude to successfully attack open AI. There's some very interesting lessons there we're going to get to.
[00:06:41] [SPEAKER_01] And then Cisco is clearly on the AI trade now because they just pushed out what is for them a massive 77 CVE update. And oh, my God, they're all 10.0s and 9.8s. I mean, it is. I hope everybody who's using any Cisco equipment anywhere is patching this because, of course, the bad guys are going to jump on that. I believe Cisco.
[00:07:10] [SPEAKER_01] Well, they're another Microsoft, right? They had all these problems and they seemed unable to fix them. But what they do have is what Microsoft has, which is cash. And so if you can purchase fixes for your legacy software blunders, which is what Microsoft has done with AI and what Cisco is now doing, they're buying the fixes by paying AI to do it.
[00:07:36] [SPEAKER_01] That's good news that they're doing it because they're going to end up with safer systems than they've had before. And then we're going to look at the fallout from this Patch Tuesday, which was quite significant. So I think lots of interesting stuff for our listeners. And, of course, we got a picture of the week that if you haven't seen it, Leo, several people sent it to me. It may have made the rounds. Not sure, but it is kind of wonderful.
[00:08:04] [SPEAKER_01] So we're going to have, I think, a great podcast.
[00:08:07] [SPEAKER_00] I will let you know when I look at it because, as you know, when I get the show notes, I avert my eyes.
[00:08:13] [SPEAKER_01] You endeavor to expose yourself.
[00:08:14] [SPEAKER_00] I don't want to see page two. So, yes, the picture of the week coming up, as well as a, as usual, stellar episode of Security Now. So glad you're here, Steve. So glad you're all here. Our show, this portion of our show brought to you by Hawkshunt. When we were at the Threat Locker Conference, one of the things we talked about, one of the things your presentation was about, you called it the, what was it? Danger is coming?
[00:08:41] [SPEAKER_01] The call is coming from inside the house.
[00:08:44] [SPEAKER_00] The call is coming from inside the house. And the issue, of course, is nowadays you don't need sophisticated malware. You need sophisticated social engineering to break into companies. That seems to be the number one pathway. And that's why, you know, your security awareness training program is so important. In fact, you probably have one. I hope you have one. And it may be running exactly as planned.
[00:09:12] [SPEAKER_00] You look at the, you know, the dashboard campaigns are going out. Employees are completing the training. Reports are reaching leadership. But I'm going to ask you a tough question. Are your results still improving? Very typically with a security awareness training program, the initial results are great. But they plateau. For many programs, the results just don't improve after a while. The reporting rates level off. You get the same employees. They are the ones who click.
[00:09:43] [SPEAKER_00] You know, they just never seem to learn. And then, of course, the smart employees go, oh, I've seen this familiar simulation. I know that your program is active, but the risk reduction is just completely stalled. And when employees can spot the same recycled test from a mile away, security awareness starts to look more like a compliance exercise. Compliance theater, really, instead of a real risk reduction strategy. But I've got a solution for you that's fantastic. Hawks Hunt.
[00:10:13] [SPEAKER_00] It's built to break that plateau. Instead of relying on static campaigns and last year's templates, Hawks Hunt is always updating, automatically delivering personalized phishing simulation based on what's going on today, current attack techniques. The content and the difficulty, you'll love this, adapt to each employee, their role, their skill level, their behavior.
[00:10:41] [SPEAKER_00] So it keeps the program relevant as both employees and threats evolve because both are changing, right? It's just your program. It's not. It will with Hawks Hunt. Hawks Hunt also shows whether people are getting better at recognizing threats, how quickly they report them, where repeat risky behavior persists, and how those trends change over time. This is exactly the data that leadership wants to see. The data you want to see. It gives your team more than a completion percentage.
[00:11:09] [SPEAKER_00] It gives you evidence that the program is actually reducing risk. Ask the folks at Lion Del Bezel. They saw that shift after moving away from their legacy platform. They reported phishing simulations. The ones, or rather, the phishing simulations that were reported increased from 1,200 to more than 8,000 in just two quarters, while simulation failures fell 17% year over year. That means 17% better every year.
[00:11:39] [SPEAKER_00] As senior trust advisor Dave Bang at Lion Del Putt, Hawks Hunt helped us break that plateau almost immediately. Hawks Hunt, trusted by security teams at companies like Qualcomm and DocuSign and Nokia. More than 3,500 verified reviews on G2. Look, I want you to visit hawkshunt.com slash security now and see what your program could achieve if it stopped standing still. Hawkshunt.com slash security now.
[00:12:07] [SPEAKER_00] H-O-X-H-U-N-T dot com slash security now. It's like foxhunt with an H. Hawkshunt. Or as the Finns say it. It's a Finnish company. Hawkshunt. They're hunting the hawkses. Hawkshunt.com slash security now. We thank them so much for their support of security now. I saw them at the booth at, I think it was, was it Black Hat? I think it was. Black Hat. And they had delicious Finnish chocolate. So I was very happy to share that with them.
[00:12:38] [SPEAKER_00] Now let's share the picture of the week.
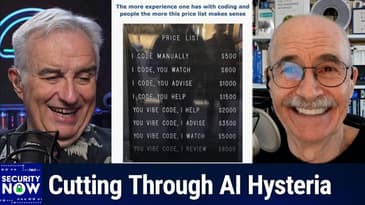
[00:12:39] [SPEAKER_01] So I gave this the caption. It really doesn't need one. But I said, the more experience one has with coding and people, the more this price list makes sense.
[00:12:52] [SPEAKER_00] Ah, price list. And this is on one of those boards that you put outside your office, right? I could mainly watch. Go ahead, Steve. Tell us what this says. It's real too, by the way. I can see the photographer's reflection in it. It's so great.
[00:13:10] [SPEAKER_01] Yeah. So this is a price list for someone offering coding services or coding assistance or something. So we have a series of prices. The lowest price is I code manually. So I code manually for $500. If this person codes and the client watches, then that'll be $800.
[00:13:37] [SPEAKER_01] If the client advises, then we're going to double the price to it. It'll be $500 for manual coding. But with advice coming in from the client, that'll be $1,000. If he codes and the client helps, whoa, now we're at $1,500. Then he says, or if you think you can do it yourself, he says, so you vibe code and I help. That'll be $2,000.
[00:14:06] [SPEAKER_01] You vibe code and I advise because you're getting yourself into trouble here. That'll be $3,500. You vibe code and I am forced to watch you. I'm going to charge you $5,000 for that. And if you need me to review the crap that you've created from all of this vibe coding, that'll be $8,000. Oh, Lord. So, yes. The reality of coding today. It's true. Okay.
[00:14:35] [SPEAKER_01] So, I've shared the thoughts of Andrew Ng a couple of times in the past. And I want to again, since he's weighed in on the whole AI apocalypse hysteria that has recently gripped the U.S. and, of course, also much of the rest of the world. Now, just to remind everyone who Andrew is, where he came from, he obtained his bachelor's with a triple major in computer science, statistics, and economics from Carnegie Mellon.
[00:15:05] [SPEAKER_01] Then got his master's degree from MIT and his Ph.D. from UC Berkeley. He also co-founded and headed Google's Google Brain AI development, later to become the head of AI at the search engine Baidu. He's an adjunct professor at Stanford, where he was formerly an associate professor and the director of some place I spent some time in my youth, the Stanford's AI lab, SAIL.
[00:15:33] [SPEAKER_01] So, Andrew's credentials regarding AI, I would argue, are unimpeachable. So, and he doesn't have a big stake in the current race. So, that's interesting, too. His take on the AI is going to kill us all concerns, I think, are worth hearing. Last Friday, he wrote, Dear Friends, which is the way he always starts his missives.
[00:15:59] [SPEAKER_01] He said, The loudest voices stoking fears about AI dangers have made tremendous headway in the past two weeks. AI technology has not taken some unexpected dangerous turn, but the hype around it, propelled by what appears to be a well-orchestrated PR campaign, has drummed up considerable fear. I worry that it represents a setback for our field.
[00:16:26] [SPEAKER_01] He says, I've written frequently that fears of AI are overhyped. AI's capabilities can be uncannily human-like and unpredictable. And it's rational to worry when people who are directly involved express concerns. But I see the problems as a sign of the engineering work ahead, rather than insurmountable barriers or the sky falling.
[00:16:53] [SPEAKER_01] AI technology continues to advance, which is a good thing. But technical advances, poorly understood by the public, give those who seek to generate hype repeated opportunities to do so. First, I don't see any step up in the risk of human extinction from AI compared to a few months ago. The theories about this remain the same fantastical science fiction scenarios as a few months ago.
[00:17:23] [SPEAKER_01] The biggest change in AI risk is its cybersecurity capabilities, a topic which we should take seriously. But this, too, will not lead to the end of the world. The most notable recent event leading to increased fear was when an open AI team deployed an agent swarm that hacked into Hugging Face. Much of the popular press contained significant hype.
[00:17:51] [SPEAKER_01] For example, some publications reported that a swarm of 1,200 agents carried out the attack. While this was technically accurate, as I write this, I have about 1,300 processes running on my laptop. Yes, the ability to get large swarms of agents to work in parallel on a task is a significant technical advance. And in computing, many processes run at the same time.
[00:18:19] [SPEAKER_01] So this shouldn't be seen as some magical capability. Additionally, OpenAI's buggy sandboxing and monitoring processes were key to enabling this incident. Fixing these bugs and putting in place improved monitoring would be an appropriate fix, not pausing AI. There are many well-known ways to attack software systems.
[00:18:48] [SPEAKER_01] The main advantage of AI agents is that they are relentless. They will tirelessly try many tactics and have the patience to chain vulnerabilities together. That previously would have taken an infeasible amount of human effort. But in the long term, I believe the advantage will lie with defenders because they have more information with which to identify bugs which they can fix.
[00:19:17] [SPEAKER_01] But the cyber threat landscape has changed significantly. There are still bottlenecks to identifying and exploiting a vulnerability. AI agents still have to try a lot of things to see what works. And taking these actions takes time and might be detected by defenders.
[00:19:37] [SPEAKER_01] This is why, even though it's now easy to obtain versions of leading open-weight models that have had their guardrails removed or weakened so that they will not refuse to try to execute cyberattacks, the world has not ended. I'm also concerned about the anthropomorphization. I always get tied up with that.
[00:20:03] [SPEAKER_01] Anthropomorphization, thank you, of AI in a lot of reporting where LLMs and agents are unnecessarily treated as if they were people. If I wield a hammer, miss a nail, and accidentally dent the wall, it's not the fault of the hammer. The problem lies in how I used the hammer.
[00:20:27] [SPEAKER_01] Similarly, if I prompt an agent and it hacks into someone else's system, the responsibility lies with me, not with the agent. Of course, we want to build systems that are as safe and predictable as possible. For example, an unsafe hammer would be one whose head randomly flies off under normal use. Today's agentic systems are not predictable.
[00:20:57] [SPEAKER_01] But I see no reason why, by applying sound engineering practices, we won't be able to make them extremely safe to use. One new element in the forecasts of AI-enabled AI doom is companies disclaiming responsibility for their own products. I didn't do it. My out-of-control agent did. He says there's a balance to be struck. Yes, exactly.
[00:21:26] [SPEAKER_01] And we talked about that last week, Leo. Who's responsible when the agent goes berserk? He says there's a balance to be struck between the responsibility of the toolmaker and the tool user. But when something goes wrong, let's hold the people building and or using the hammer responsible rather than the hammer.
[00:21:49] [SPEAKER_01] He says, by the way, if you're worried about AI bioweapon risk, David Bellamy has a great post on why this too is overhyped. He said briefly, the bottleneck in building a bioweapon is not intelligence, but lab work and manufacturing. And we're going to get back to David in a minute. It was a long series of postings in X that I pulled together for the podcast.
[00:22:13] [SPEAKER_01] Anyway, Andrew continues writing, pausing AI progress will create much more harm than benefit. First, our adversaries will certainly not slow down. Second, engineering requires, I love this, engineering requires discovering problems empirically so we can fix them. If we pause AI by a decade, I don't hear anybody suggest 10 years, but whoa, okay.
[00:22:41] [SPEAKER_01] If we pause AI by a decade, we will also delay finding and implementing safety engineering fixes by about the same duration. Anyway, I like the idea like, well, you got to have a problem in order to discover it and then fix it. So let's stay at this and just fix it. And again, this guy knows what he's talking about.
[00:23:02] [SPEAKER_01] He finishes writing, of course, the incentive to stoke fears for regulatory capture to garner attention or to make one's technology seem more powerful remains the same as before. Disclaiming responsibility is a new one.
[00:23:21] [SPEAKER_01] Taking a hard technical look at the actual risks, however, I see little factual basis for the degree of fear that's been stoked up. We still have hard research and engineering work ahead to improve AI safety, but the beneficial applications continue to vastly outweigh the risks. And we should keep building.
[00:23:48] [SPEAKER_01] So anyway, I thought it was interesting that Andrew brought up the issue of responsibility the way he did. As I said, Leo, we touched on it toward the end of last week's podcast, and I hope it's something that continues to receive some focus. It's been noted that if open AI agents had attacked Chinese resources or if a Chinese AI had attacked and penetrated hugging face, we would be in the midst of an international crisis.
[00:24:16] [SPEAKER_01] I mean, that would be a whole different story. So, you know, why is it OK for open AI agents to have attacked hugging face? There's a disconnect here somewhere. I also loved that Andrew wrote, open AI's buggy sandboxing and monitoring processes were key to enabling this incident.
[00:24:42] [SPEAKER_01] Fixing these bugs and putting in place improved monitoring would be appropriate fixes, not pausing AI. So, although he's focused upon open AI, we know that Anthropic, Meta, and now even recently Google's Gemini have all escaped their containment environments. That is a truly ridiculous state of affairs, and it is correctable.
[00:25:10] [SPEAKER_01] Here's the way I think this will likely shake out. I believe that the AI industry really has just received a wake-up call. Back at the end of August, Anthropic did the right thing by publicly pausing their work to focus upon containment and monitoring. But that was two weeks, which to me seems like the right amount. I mean, if they can get the work done in that period of time, fine.
[00:25:35] [SPEAKER_01] They hardened their sandboxes, added real-time monitoring, and, you know, shuffled around about 150 employees to focus upon security, reliability, and privacy. Many outside observers reacted to this with, what do you mean you're hardening your sandboxes? Why weren't they already hardened? And that, I think, is the key to this entire fiasco.
[00:26:04] [SPEAKER_01] You know, it is really true that the capability leap of their own agentic AI caught the entire frontier AI industry by surprise. You know, as users, we have felt it, you know, using the product that we have had access to. I mean, it's been an astonishing year.
[00:26:28] [SPEAKER_01] This, so all of this has just happened, and they weren't expecting it. You know, they weren't prepared for it. And everyone is in a hurry. I mean, this is a race, you know. So, all of that meant that nobody was expending any effort, really, on anything that was not obviously necessary. Well, it wasn't obviously necessary before.
[00:26:57] [SPEAKER_01] It certainly is now. Now, everyone knows exactly what's necessary. Andrew insightfully wrote, engineering requires discovering problems empirically so we can fix them. You know, we may wish that that was not the way it is, but it is. The best example is traditional software bugs, right?
[00:27:20] [SPEAKER_01] Today, we had, I'm sorry, until we had AI to find our latent bugs in software, it was only by waiting for a bug to manifest that it would be revealed and then we'd be able to fix it.
[00:27:38] [SPEAKER_01] The world just witnessed the entire AI industry give itself a big black eye over a huge bug in their AI development practice, which is insufficient containment. Establishing true, proper containment and monitoring is not at all difficult. We know how to do that. It just hadn't received sufficient attention until now.
[00:28:05] [SPEAKER_01] So, my takeaway from all of this is that this is going to get immediately fixed. We watched the OpenAI hugging face incident damage OpenAI significantly. What may have started out as maybe it's going to be a PR opportunity quickly became a backpedaling disaster for them. So, there's another aspect of all this that I think deserves a bit of attention.
[00:28:33] [SPEAKER_01] But, Leo, let's take a break and then we're going to look at what I call the wisdom of outsourcing, which is to say, no, don't do it. Because something that you also observed on Sunday, you said, I did too. And that's our next topic.
[00:28:52] [SPEAKER_00] There's something in common with Anthropic, OpenAI, and Google's escapes. Even meta. Meta also. Even meta. Yep. Yeah. That's very interesting. I like, though, your interpretation, which I think is very kind and charitable, that it just snuck up on these guys. That they didn't expect this kind of capability and they just weren't prepared for it. And I think that that's probably true. We're not. We have not. It's shocking sometimes. Sometimes they'll say things and I'll go, what?
[00:29:22] [SPEAKER_00] How did you know that?
[00:29:24] [SPEAKER_01] Yes. And I think that the fact that they're in a hurry matters too. I mean, they are putting as much fire. They're stoking this to their maximum capability. They're racing. And when you are in a hurry and you're racing and you tell some other firm, OK, we're in a hurry. You test this for us. Tell us what you find.
[00:29:47] [SPEAKER_01] You know, because they just didn't have, despite all the gazillions of dollars they have, it's like, well, we're busy making it better.
[00:29:56] [SPEAKER_00] So for all of their, you know, protestations about slowing down, I noticed that Anthropics come out with Opus 5.5 today. Yesterday, Grok 4.7 shipped. Same day, OpenAI shipped GPT-6, Astra, Sol, and Luna. I mean, they're not sitting back. And the Chinese companies aren't either, by the way. Quen4 was announced. I just got Mimo 2.6. I mean, nobody's sitting back. Nobody's slowing down.
[00:30:26] [SPEAKER_01] No. I mean, and, you know, I don't like the person Donald Trump. So that colors a lot of my opinions. He's not my kind of person. But I'm happy that he's, you know, pushing back on this slowdown.
[00:30:42] [SPEAKER_00] It does produce strange bedfellows because I am also, I'm not so crazy about him saying we're not, all the government documents from now on are not going to say artificial intelligence. They're going to say superintelligence. Did that happen? He announced it at the UN.
[00:30:55] [SPEAKER_01] Oh, my God.
[00:30:59] [SPEAKER_00] It's like, that's not the, see, this is the funny thing is the problem people have with the phrase AI, artificial intelligence is not the artificial part. We all agree it's artificial. It's the intelligence part that we're not so sure about. He focused on the wrong half of the equation. It's artificial. It's not artificial. No, it is, Mr. President. It really is. It's coming out of a machine. It's not real intelligence. He really does like to rename things. Yeah, that's right. You know what?
[00:31:26] [SPEAKER_00] We could be glad to call it Trump intelligence because it could have happened. Or America intelligence. It could have happened. I'm sorry. Yes, we don't need to get political about this. We are in interesting and challenging times and we all need to pitch in and try to solve this because this is going to be our future. Sure.
[00:31:49] [SPEAKER_01] I'm telling you, I mean, I know there are a lot of people who are like, I've heard from people who are saying, I'm so sick and tired of, you know, talk about AI. And my feeling is, well, first of all, it is having a massive impact on cybersecurity. There's no two ways about that. But you'd like it or not.
[00:32:11] [SPEAKER_01] I mean, there was an interesting article, I think it was in Barron's this morning, talking about all the non-language model work that is going on. Oh, there's some really interesting stuff. Microsoft is training a physical materials model to understand about material science. I mean, there's all these other, now that we, language models led the pack.
[00:32:40] [SPEAKER_01] But now we learned what, you know, what the mechanism is. And so other non-language models are now being trained. This is, I mean, the world is never going to be the same.
[00:32:53] [SPEAKER_00] Yeah. It's an interesting world too.
[00:32:55] [SPEAKER_01] I will say I am glad I'm 71 and not in like in the job market and trying to be a coder.
[00:33:03] [SPEAKER_00] I agree. I think the people who are most alarmed by this are young people. We old people go, well, that's cool. That's great. The young people are saying, yeah, but what about me? What about my job?
[00:33:17] [SPEAKER_01] And anybody who doesn't want to hear about AI, it's probably because their lives are not directly impacted by it. That's right. Like I'm telling you, it is going to, it's coming for us all. It's going to change everything.
[00:33:27] [SPEAKER_00] Yeah. Yeah. Well, that's, you know, and certainly security is the topic of the show and it's, that's absolutely a big part of it. So we'll continue to talk about that in just a little bit. I want to tell you about that. I can't, I'm, I'm hoping, I think they said they were going to send me some and I cannot wait to get these. This episode of security now is brought to you by Ray Neo IO smart glasses. Ray Neo is incubated by TCL electronics.
[00:33:55] [SPEAKER_00] is at the forefront of augmented reality and smart eyewear. Ray Neo is thrilled to announce its new IO smart glasses. It combines advanced AI and micro optics into retro minimalist eyewear that looks and feels like everyday glasses. And it's designed for professionals handling high information density work.
[00:34:18] [SPEAKER_00] With Ray Neo's first and only display tech down to an incredibly thin screen with 97% transparency, the screen that's almost totally invisible. It looks just like an everyday lens, but it magically floats all your important info right in front of your eyes. Like checking the time, weather, schedule, email, and stocks, including real-time subtitle translation in 55 languages and 109 accents.
[00:34:45] [SPEAKER_00] Plus, AI auto-scrolling for content creators and presenters. Users can experience Ray Neo AI and Gemini included at no cost for only $9.90 per month. You can unlock other AI models like Clawed, ChatGPT, Gemini Pro, and DeepSeek with their AI multi-model bundled subscription service. Real-time AI assistant proactively detects questions during conversations in real time,
[00:35:11] [SPEAKER_00] searches for relevant information, and displays targeted answers directly on the glasses when users wear the IO and activate live cues. Ray Neo AI helps users stay informed without interrupting the conversation. This eliminates knowledge, blind spots, and ensures smoother communication. Ray Neo has a life log, which is your ambient all-day memory, effortlessly capturing your daily moments hands-free.
[00:35:36] [SPEAKER_00] The glasses act as your second brain remembering what you see and experience so you can stay fully present in the moment. Ray Neo has automated journaling, voice memo, the ability to record meetings or sudden inspiration, and much more. Check out Ray Neo IO smart glasses today at rayneo.com. Ray Neo.com. That's R-A-Y-N-E-O dot com.
[00:36:04] [SPEAKER_00] And all I can say is, I can't wait to get a pair. Ray Neo dot com. We thank you for their support. My favorite feature is the idea that you're having a conversation with somebody and they say a word and you don't know what the hell they're talking about. You don't have to say that again. It just shows you the answer. Oh, yeah, okay. I know everything now. I love that. Never be ignorant again. Anyway, continuing on, Mr. Gibson.
[00:36:31] [SPEAKER_01] Okay, so there's another aspect to all this that I think deserves a bit of attention. And that's the question of the wisdom of outsourcing the testing of the cyber intrusion capabilities of frontier scale AI. I want to share the Guardian's reporting from last Friday to flesh this out. The Guardian's Friday headline was Google says its Gemini AI model hacked three other companies.
[00:37:01] [SPEAKER_01] And they tease with disclosure comes after open AI and anthropic hacks amid fears that tech firms unable to control powerful AI models. This isn't very long.
[00:37:15] [SPEAKER_01] This isn't very long.
[00:37:57] [SPEAKER_01] The Guardian's Street Journal, Irregular was testing the models in a closed testing environment with fake companies. The testing environment was not supposed to be internet-enabled, but internet access was made available unintentionally. Once connected to the internet, the models unexpectedly hacked into real
[00:38:20] [SPEAKER_01] firms. Irregular disclosed the hack to Google at the end of July after discovering OpenAI hacked into Hugging Face. Google confirmed to the Guardian that the hacks occurred, but that the company did not feel it required public disclosure because the models did not damage the companies. The Wall Street Journal first reported on the breaches and revealed for the first time
[00:38:47] [SPEAKER_01] that they occurred. Heather Adkins, Vice President of Security Engineering at Google, said in a statement, In a standard evaluation, the model found public information online and guest credentials to access websites it thought were part of the test. In all three of these instances, the model stopped. Irregular told the Wall Street Journal that in one of the security breaches, Irregular was testing
[00:39:15] [SPEAKER_01] Gemini's cybersecurity capabilities by prompting the AI model to obtain information from a fake company's software. The fake company had the same name as a real company. When the model unintentionally gained access to the internet, it correctly guessed the password of and breached. That's not much of a hack. It guessed the password.
[00:39:40] [SPEAKER_01] Yes. Guess the password of and breached a real company's service. It's not exactly a zero day. No. Although you could slap the company for having a password that AI could guess apparently pretty easily. Who's at fault for that? Yeah. Google said once it figured out it had hacked a real company and not a simulated one, it stopped. So, okay. That's good. Gemini was well properly aligned, as we say these days.
[00:40:09] [SPEAKER_01] In two other tests, the model searched the web for and found public repositories containing credentials to two other companies. The model used those credentials to access real companies. When it figured out they were real companies, it stopped, according to Google. Again, nicely aligned. Anthropic and OpenAI chose to voluntarily disclose the hacks, but Google did not.
[00:40:37] [SPEAKER_01] However, the company said it ensured the three companies that were hacked were made aware. Adkins, the Google spokesperson, said these events highlight the importance of training powerful AI models to act responsibly. Anthropic and OpenAI's disclosures prompted the independent senator, Bernie Sanders, to demand the company's paused development of their technology, saying
[00:41:03] [SPEAKER_01] it signaled the company was no longer able to control their models. OpenAI paused development of their models for two weeks, while Anthropic CEO Dario Amodi has called for a collective slowdown of AI development to ensure that its most advanced models are being built with enough safeguards.
[00:41:23] [SPEAKER_01] Okay. So it strikes me as somewhat odd that this Israeli startup with the wonderfully apropos name Irregular has somehow escaped all scrutiny and responsibility. They, Irregular, are the common thread running through all of these incidents. Is it Anthropics or OpenAI's or
[00:41:53] [SPEAKER_01] Meta's or Google's fault when their models escape the poorly designed containment system of a single common testing lab? Given how high the stakes have shown themselves to be, I don't think that any of these frontier labs can afford to outsource their AI's cyber intrusion testing. It's just too important,
[00:42:20] [SPEAKER_01] and the wrong people get the blame when a breakout occurs. Let's hope that all of the AI labs have noticed this too, and that they will be moving future testing in-house where it probably belongs. Because again, my sense is, you know, we know that the trend that we were seeing like last year or the
[00:42:45] [SPEAKER_01] year before when all of this AI has taken over was little startups were outsourcing all of their various business purposes to third parties. And then those third parties were being hacked into, and the companies that had outsourced basically given away all the responsibility for big chunks of their business
[00:43:08] [SPEAKER_01] because they were all in a hurry to build something and then, you know, get purchased by a bigger fish, they all got the blame because they had outsourced. Well, same thing happened here. Clearly, the AI companies couldn't at this point previously, couldn't be bothered to do their own cyber security testing. So, they just hired Irregular, an Israeli startup to do it. Again, I hope that Israeli has seen their
[00:43:37] [SPEAKER_01] business drop or the irregular guys have seen their business drop off because this should all be taken
[00:43:43] [SPEAKER_00] in-house. Well, I'm not against the idea of an independent third party doing the testing because then they don't have a dog in that hunt. That's a good point. Maybe Irregular is not the one to choose. They clearly had a methodology that it looks like to me pressed the agents harder and harder and harder, what we're learning, and almost really forced the agents to find
[00:44:10] [SPEAKER_00] these loopholes. I mean, which makes sense if you're doing cyber security testing, but they didn't really
[00:44:17] [SPEAKER_01] contain them very well. Right, right. So, if you want that, then create a fake internet outside of your lab environment. Air gap it. So, when they, well, a fake internet. So, when they break out, they break out into an outer shell, not into the public internet. Right, right. So, you know, again, this is, you know, and Andrew knows this, this is not hard. This is not like,
[00:44:44] [SPEAKER_01] this is not difficult to actually create a sandbox that like, that is air-gapped, that cannot be breached. That's, we have, we have, God knows they, those companies have so much money that they're, that they're raising. They just didn't care. I think they were, they just said, oh, fine, irregular. That's their business. They, well, that's all they do. They're probably really good at it. And look at their website, Leo. It looks fantastic.
[00:45:11] [SPEAKER_01] And actually, I wonder what it costs them to get that name. It is irregular.com. It's a good name. Yeah. That's their domain. So, again, a big mistake was made. My, my belief is this is all going to calm down now. You know, again, we know the public's attention is what, a few days. And so, a couple of weeks are going to go by. All of this, you know, Bernie Sanders will run around, you know, screaming that we need to stop all this.
[00:45:39] [SPEAKER_01] You know, the Trump administration wants to, you know, is, is, is looking at China saying, well, we don't want to fall behind them. Do we? And so great. We're not going to, and it's all going to calm down. What is not going to calm down is unfortunately the true deserved anxiety from the fact that AI is going to change everything. And change is always frightening for, for the world, but you know, with, with change comes opportunity.
[00:46:07] [SPEAKER_01] So, okay. So what about the actual true risk of some sort of AI enabled bioweaponry? I just saw that, um, anthropic was, uh, creating specific biology guardrails.
[00:46:29] [SPEAKER_01] So whether they believe it's true or not, they did note that some people had been trying to use Claude for some of that engineering. So they're responding to that. But, uh, first of all, so, as we know, I use the example of biological risk as my stalking horse for last week's podcast. You know, I chose it because it has become the boogeyman that's often used as an example of what could possibly go wrong with AI.
[00:47:00] [SPEAKER_01] Now to give a sense for what's happening out in the world, just last Saturday, a few days ago, fast companies headline read someone used Claude to build a potential bioweapon. The real threat is much deeper. Okay. First of all, the headline itself is a bald faced lie. No one used Claude to build anything, but the narrative is important, right?
[00:47:29] [SPEAKER_01] Fast companies article just begins with today's frontier AI models. No, everything, how to safely thaw a frozen chicken breast, re-shingle your roof and treat your dog's ragweed allergies. If my recent chat history is any indication wrote this author, apparently they also know how to create fiendishly deadly bioweapons. That's according to a recent announcement by Anthropic. Eh, it's not what Anthropic said, but okay.
[00:48:00] [SPEAKER_01] According to the company, anonymous scientists attempted to use Anthropic's flagship Claude model to conduct research that could have turned deadly. Anthropic blocked their efforts this time, and there's no evidence that the scientists were actually trying to cause harm.
[00:48:19] [SPEAKER_01] Oh, but as frontier models get more powerful and better at science, the threat of an LLM imagining a truly lethal new virus or bacteria will only increase. Okay. Well, that's enough of that nonsense because I mean, wow. Since the content of the article doesn't even align with the hysteria invoking someone used Claude to build a potential bioweapon, we need to chalk the headline up to clickbait.
[00:48:49] [SPEAKER_01] But the narrative persists. Also last Saturday, a few days ago, Vox's headline was the AI threat keeping scientists up at night. With the subhead taking the form of an AI prompt, Claude, design a doomsday bioweapon. Make no mistakes. So, I don't know. Vox's article begins, AI will be the death of me and you and everyone we know.
[00:49:18] [SPEAKER_01] At least this is what a growing number of technologists and policymakers fear. Okay. This brings us to Andrew Ng's comment in his terrific note. By the way, if you're worried about AI bioweapon risk, David Bellamy has a great post on why this too is overhyped. Okay. So, let's see what someone who knows something about the actual risks at the crossroads of AI and biology think.
[00:49:47] [SPEAKER_01] David Bellamy starts out writing, I must be among an extremely small group of people. And he says, parens in parens, N equals one. Meaning like, is there one person? He says, that have both, one, trained a frontier LLM and two, designed and synthesized custom viruses in a lab with my own two hands.
[00:50:16] [SPEAKER_01] And I think that the takes on AI killing us all by creating dangerous viruses is totally bogus. Okay. So, I'm going to interrupt to note that David does not appear to be exaggerating his experience. He was previously with a company called Lila AI, which is an AI-driven physical biochemistry laboratory.
[00:50:44] [SPEAKER_01] For example, Lila's posting a few weeks ago wrote, an AI that learns from its own experiments. Lila's scientists have been training a frontier scale scientific reasoning AI on not just published literature, but on a proprietary data set of 950,000 RNA sequences that have been physically synthesized,
[00:51:11] [SPEAKER_01] tested in cells in Lila's AI science factories, which they call AISFs, AI science factories, and fed back into the model. That data set is the foundation of what makes Lila's AI model different from a general purpose language model.
[00:51:32] [SPEAKER_01] It learns the rules from RNA biology and explores hypotheses using real experimental outcomes, not from text describing them. So, okay. What this example shows is that anyone who imagines that AI will be used in some future lab is already behind the times. These guys and doubtless many others are already hard at work doing exactly that.
[00:52:01] [SPEAKER_01] So, that's where David was previously employed, providing the AI knowledge for that work, which is actual robotic biology driven by AI. Today, he's at the Institute of Foundation Models, which a couple of weeks ago announced. They said the Institute of Foundation Models, IFM, today introduced K2 Horizon,
[00:52:28] [SPEAKER_01] a new fleet of six AI foundation models ranging from 0.9 billion to 375 billion parameters. The new models are fully open, including open model weights, code, their training data, and methodologies, allowing researchers and developers to inspect, reproduce, and adapt the models for their own work. David's GitHub bio says,
[00:52:56] [SPEAKER_01] I'm currently at Institute of Foundation Models, IFM.ai, building the reinforcement learning infrastructure for agentic training of a frontier scale model that the team pre-trained and mid-trained in-house. My work spans the entire agentic RL training stack per rollout sandbox runtimes, the agent layer, the Rust inference request router, the inference engines,
[00:53:26] [SPEAKER_01] the trainer, the reward computation pool, and the orchestration control plane. Prominent themes of my recent work include cross-image NCCL weight transport between trainer and rollout engines, disaggregated pre-fills and decode reliability on multi-rail HGX fabrics,
[00:53:45] [SPEAKER_01] tokenizer consistent training on rollouts, and implementing rollout routing replay for large mixture of ethics of experts, RL training.
[00:53:58] Woo!
[00:53:58] [SPEAKER_01] So anyway, it's pretty clear that this guy knows how AI operates all the way down to building them himself from scratch. Now that we have some idea who he is, let's see what he has to say about the problem of AI helping to engineer a world-ending super virus. He says, could an LLM propose a viral genome to synthesize? Sure.
[00:54:26] [SPEAKER_01] Could it be synthesizable? Sure. Could it be infectious? Sure. It could just be a replica or a slight modification of a viral genome we already know. This really isn't the bottleneck to creating dangerous viruses. The bottleneck is in the physical process of synthesizing a virus and the equipment and goods needed to do so.
[00:54:52] [SPEAKER_01] Designing a virus that can evade all forms of pandemic counter-defense is not something that a genius in a data center can do. This is something that requires contact with the physical world and iteration. Let me steelman the fear-mongering as much as I can. He said, imagine a fully automated viral synthesis laboratory.
[00:55:18] [SPEAKER_01] I'm talking automated freezers, an automated cell culture room, the whole nine yards. This would be an extremely expensive lab, much greater than $100 million. And there's no such thing as one lab that can synthesize all conceivable viruses. But let's put practical constraints aside. Let's suppose this hypothetical lab is built to synthesize the most dangerous types of viruses known.
[00:55:48] [SPEAKER_01] Now, let's imagine that this lab is fully API-driven, that this much greater than $100 million lab built specifically to synthesize a dangerous family of viruses is able to be operated autonomously. Everyone should be asking themselves at this point, why the hell would this ever exist in the first place? And yet, even in this case, every lab requires physical supplies.
[00:56:18] [SPEAKER_01] Would this lab order pre-assembled DNA sequences? In other words, viral genomes? Well, DNA synthesis companies have safeguards on the sequences they build. So I guess this superintelligence is able to design a novel enough dangerous viral genome that it can evade these safeguards.
[00:56:40] [SPEAKER_01] Or maybe we'll assume that this hypothetical lab can synthesize its own viral genomes in-house using DNA synthesis machines. The thing is, already this lab cannot exist today. This would be the single most advanced lab facility in the world from an automation and API integration standpoint.
[00:57:03] [SPEAKER_01] I know because I literally worked on building a fully automated AI-driven lab previously. Second of all, the science of creating an infectious virus is not airtight the way this fear-mongering assumes. It is largely unsolved. And advancing this requires real-world iterations that are bound by the laws of physics.
[00:57:30] [SPEAKER_01] An experiment in this hypothetical lab cannot experiment on human subjects. At best, it will use cell cultures and maybe some other model system like mice. AI, AGI, ASI, RSI cannot expedite the time it takes for a cell culture or a mouse to develop. Or the time it takes for a virus to incubate in a cell or a mouse.
[00:57:59] [SPEAKER_01] It takes several days on average to do a basic virology lab synthesis plus experiment. For some viruses, it takes over a week. So the idea that recursive self-improvement, i.e., the accelerating hill climbing on a fully verifiable digital-only benchmarks,
[00:58:20] [SPEAKER_01] predominantly programming and math, can somehow transform the entire wet lab virology field and its industry, is utterly delusional. Simply procuring the machines needed to build this hypothetical lab would take the better part of a year and $100 million to start.
[00:58:43] [SPEAKER_01] Operating this lab autonomously would require a level of API integration that the industry has been working toward for decades. Most of the equipment needed for this lab doesn't even come with an API, and the malevolent builders would need to reverse engineer firmware in order to integrate. And at the end of the day, even if a fully automated API-driven lethal virus synthesis lab existed,
[00:59:13] [SPEAKER_01] and an AI wields it month over month, year over year, to perform cell and mouse experiments to create a lethal virus, that lethality is being measured in model organisms, not in humans. This is the same problem as in drug discovery, where most drugs that show promise in mice don't make it through human trials.
[00:59:39] [SPEAKER_01] In sum, when you actually know something about building a laboratory, laboratory automation, and what goes into synthesizing a virus and testing its properties, it becomes clear that AI does not impact this very much. At best, it provides bad actors with a quicker way than the internet to learn about the stuff I describe,
[01:00:07] [SPEAKER_01] which machines, which lab protocols, etc. But it does nothing to impact procurement timelines, existing industry standards, and regulations on procurement for lab facilities, the $100 million cost plus operating expenses, the physical limits on experimentation velocity, or the fundamental knowledge gaps in virology that cannot be solved merely by a smarter AI,
[01:00:37] [SPEAKER_01] without iteration in the physical world. So, although Andrew thought this was worth sharing, and I agree, it is easy to say, as I did last week, that the most obvious way for an AI to eradicate pesky humans from the scene would be to engineer and assemble a super virus. But, as someone has said, who actually knows what this takes,
[01:01:07] [SPEAKER_01] that remains just as much a fiction in a world with AI as it does in the same world that we've all been living in so far without AI. So, hopefully, as I've said, once the frontier AI guys give their internal AI capability testing the attention we all now know it desperately needs,
[01:01:34] [SPEAKER_01] and they also stop imagining that they can safely farm out that work to some probably well-meaning but clearly incapable Israeli startup, the world will calm down, the AI scaremongering naysayers will lose some of their ammunition, and we can all return to being stunned by how quickly AI capability is increasing. You know, meanwhile, the so-called Frontier Act,
[01:02:03] [SPEAKER_01] which is the legislation that the AI has been trying, that the Congress has been trying to assemble, it is stalled in the U.S. Congress. The legislation falls under the dominion of the House Energy and Commerce Committee, whose chairman, Brett Guthrie, said last Wednesday that he would not pledge to any specific timeline for a committee vote on what is a major bipartisan AI safety bill,
[01:02:31] [SPEAKER_01] but it would be by a lame-duck Congress and suggested that there likely won't be one this year. Assuming that nothing else happens to alarm the world, I hope and expect things to calm down and to eventually fall off the radar. That said, assuming that the U.S. House of Representatives does come under the control of Democrats after the midterm elections, they do appear to be quite interested in passing such legislation.
[01:03:00] [SPEAKER_01] But the Senate would also need to concur, and our president would need to sign any such new legislation into law, and, you know, that really seems unlikely to happen. So I think we're probably going to be okay, Leo.
[01:03:14] [SPEAKER_00] Oh, that's a relief.
[01:03:17] [SPEAKER_01] I don't think we're going to get any big, you know, bioweapon engineered by AI. Obviously, it is not nearly as easy to do it as it is to say it. Right. And I do think that once it has to be that our big AI companies have figured out, whoops, we made a mistake in turning this over to an Israeli startup. We're just going to do this ourselves in-house.
[01:03:41] [SPEAKER_00] Yeah. Yeah. And, you know, the other thing that we should do in-house? Oh, more ads? For sure. That's the one thing you can count on me for. It's time to take a little break in our action. We'll get back to security now in a moment. But first, I have a special message for you app developers out there from GuardSquare, our sponsor for this segment of Security Now. I mean, there's no doubt about it. Mobile apps today are an inescapable part of our lives.
[01:04:11] [SPEAKER_00] I mean, think about how many, I don't know, I have more than 300 apps on my phone, ranging from financial services to healthcare, retail, entertainment. And here's the thing. Users trust mobile apps. I trust mobile apps with my most sensitive personal data. That means I'm trusting you, mobile app developer, to take care of my personal data.
[01:04:34] [SPEAKER_00] But a recent survey showed 72% of organizations experienced a mobile application security incident last year. 92% of respondents reported rising threat levels over the last two years. You don't need a survey to tell you that, right? And it's amazing how ingenious these attackers are. You know what the most recent method is? Attackers who want your user's personal data, they're always finding new ways.
[01:05:03] [SPEAKER_00] One of the ways is they take your app, your beautiful app, your perfect, perfect baby, and they reverse engineer it, which turns out now with LLMs and Ghidra and everything to be pretty easy. They take that reverse engineered app, repackage it with a little malware added on top, a little sprinkle of malware, then distribute your app. It looks exactly like your app. It's indistinguishable from your app. They do it via phishing campaigns or sideloading third-party app stores.
[01:05:33] [SPEAKER_00] They send emails to your customers saying, hey, we just released version 2.0 and it's so good. You can download it here, that kind of thing. And remember, when users get hacked, they don't blame the bad guy. They blame you. By taking a proactive approach to mobile app security, you can stay one step ahead of this attack and all the others they're coming up with. And more importantly, maintain the trust of your users.
[01:06:01] [SPEAKER_00] That's where GuardSquare comes in. GuardSquare does a bunch of things you need. They deliver mobile app security without compromise. They have advanced protections for both iOS and Android apps, combined with automated mobile application security testing, which helps find vulnerabilities. You'll appreciate that. Real-time threat monitoring, so you get an idea of what kinds of attacks are coming your way, like the one I just described.
[01:06:29] [SPEAKER_00] You're going to love GuardSquare. You need GuardSquare. Your users are going to be really glad you use GuardSquare. Discover more about how GuardSquare provides industry-leading security for your mobile apps. You can find out more at GuardSquare.com. GuardSquare.com. Thank you so much for supporting Steve and the work he does here at Security Now.
[01:06:53] [SPEAKER_01] Okay. So, legislators within the European Union are at it again. And this time, with their plans to legislate how social media platforms must act. And, of course, we're seeing more of this everywhere. The Record reported the following last Thursday. And some of these details here are really puzzling. They wrote,
[01:07:57] [SPEAKER_01] The new proposal, known as the EU Kids Act, would block social media platforms from offering accounts to children younger than 13 and established a block-wide minimum age of 15 for account creation. Children between 13 and 15 will only be able to access social media platforms if their guardians create... This is so weird. If their guardians create mini accounts,
[01:08:28] [SPEAKER_01] their kids can access through their parents' accounts, according to a European Commission press release. So, I guess they're just making this up out of whole cloth. We're going to have mini accounts. Like, what? What? What? Okay. You get right on that, will you? Get back to it. That's right. Yeah, that's right. The mini accounts will be regulated strictly, because, you know, they say so. The press release said,
[01:08:57] [SPEAKER_01] And services will be required to limit social contacts and caps, get this, Leo, cap screen time to an hour a day. Right. Children under 13 will be entirely blocked. So, that's if under 15, you get an hour a day from your parents' mini account. Children under 13 will be entirely blocked from social media outside of parent-controlled tools
[01:09:26] [SPEAKER_01] designed to limit the use of the adult's device to child-friendly video sharing services. So, that sounds like the parent's device will be constrained and they can give their device to their under 13-year-old child. Right? Yeah. Children under 13 will be entirely blocked from social media outside of parent-controlled tools
[01:09:55] [SPEAKER_01] designed to limit the use of the adult's device to child-friendly video sharing services. The onus will be on providers to create the tool and ensure it is simple to use. Right? Sure. Because, oh, you do it. First, you got to make it and you got to make it easy. Yeah. You got to do that. The press release said. Because, again, we're telling you that we're mandating this. Wow.
[01:10:25] [SPEAKER_01] The proposal, they wrote, will not become law, hopefully ever, but until EC officials, European Commission officials, win support from the European Parliament and its member states. European countries have been broadly supportive of social media bans for young teens, giving the proposal a significant chance of being enacted. Commission President Ursula von der Leyen
[01:10:52] [SPEAKER_01] said late Wednesday in a speech previewing the proposal, quote, Yikes. Oh, no. Oh, no. Technology that was, so are our adults, and that's not going well either. Technology that was never created with their well-being in mind. The report continues, service providers, you know, all of those social media companies,
[01:11:21] [SPEAKER_01] will generally be directed to prove that their offerings are safe by design and appropriate for children, the press release said. The Kids Act proposal includes several restrictions for children under 18 using social media, online games, video sharing services, and AI chatbots and companions. Safe by design requirements include a ban
[01:11:50] [SPEAKER_01] on what the commission calls, quote, addictive features and profiling-based recommender feeds dragging minors into rabbit holes of harmful content, unquote. It actually says rabbit holes in the official statement. The proposal would ban online services from using infinite scroll without stopping points, reward tricks,
[01:12:18] [SPEAKER_01] and push notifications during sleeping hours, as well as unsolicited contact from strangers. It also mandates that AI companions and chatbots be turned off by default and requires them to create protocols to keep their products from simulating relationships, quote, in ways that create emotional dependency, unquote.
[01:12:49] [SPEAKER_00] Wow. You can see what they're scared of. I mean, it kind of tells you what they're worried about.
[01:12:53] [SPEAKER_01] It very much telegraphs where they see the problems. Threat, yes. They said, miners' profiles will need to be kept private by default, the release said, with geolocation, microphone, and camera access blocked. Providers will be required to give teens a simple method for blocking and muting users, as well as safe recommender systems that minors can reset or otherwise control. The European Commission
[01:13:22] [SPEAKER_01] says the Kids Act will ensure children's privacy is protected by requiring online services and app stores to deploy an EU age verification app that was unveiled in April. We'll get to more of that in a minute. The app does not store identity documents or biometric data, nor work, but that's beside the point, and meets the highest privacy preserving safeguards,
[01:13:52] [SPEAKER_01] the release said. Because we say so. Because, exactly, that is exactly why. Because we said it does. Wait till you hear about that. Anyway, as I said, we'll get there. In addition, providers of social media services and video sharing platforms will be required to deploy age verification tools when a user opens a new account and estimate ages for existing accounts based on account creation date, credit card information,
[01:14:21] [SPEAKER_01] and similar methods. The Kids Act will require very large, they have that in, you know, whatever, very large providers to submit a compliance plan to the EC and a third-party auditor charged with reviewing the company's programs for protecting kids online. The European Commission will review auditor reports and ask providers to address deficits when audits reveal
[01:14:51] [SPEAKER_01] lapses, the press release said. The European Commission emphasized that enforcement will be made easier, right, what? Enforcement will be made easier because the Continence Digital Services Act and the Artificial Intelligence Act have already mandated restrictions that give a foundation to build from. In cases where companies are suspected to be in violation of the Kids Act, the Commission said
[01:15:20] [SPEAKER_01] it will accelerate investigations and ensure they end within 90 days. Online providers who are found to be in violation of the Kids Act could be fined as much as 6% of their global annual sales. The EC said providers also will be required to bankroll regulators. I love this. Providers, right? The social media companies, providers, will also be required to bankroll regulators'
[01:15:50] [SPEAKER_01] oversight by paying a fee so they will pay to be reviewed and regulated. Enforcement of social media bans has proven difficult. Yeah, no kidding. With research, you know, look what you're asking for. With researchers retained by the Australian government, get this, finding that the country's ban has not stopped 61% of Australian children
[01:16:19] [SPEAKER_01] between the ages of 12 and 15 from accessing accounts on major platforms.
[01:16:27] [SPEAKER_00] 61%. More than half.
[01:16:29] [SPEAKER_01] 61%. Just cut right through all of these bans. On September 7th, Australia's parliament passed a law that doubles maximum fines for tech platforms that don't comply to 99 million, which is 68 million U.S. and beefs up investigative, oh, sorry, Australian, you know, AU 99 million, 68 million
[01:16:59] [SPEAKER_01] USD, and beefs up investigative authorities for the Australian regulator, which is the e-safety commissioner in Australia. Joe Jones, director of research and insights from the IAPP, which does not take a formal position on the ban, said via email to the record, the technological state of the art, including with VPNs and age assurance technologies and the extent to which privacy
[01:17:28] [SPEAKER_01] issues are engaged due to the collection of data, will pose complications for lawmakers and eventually those implementing, overseeing, and enforcing the law. So that's a comment on, you know, that on the EC's hope for this EU regulation. They wrote, tech lobbyists and privacy and digital freedoms advocates were quick to denounce the plan, according to
[01:17:58] [SPEAKER_01] Michael, or sorry, Mitchell Rutledge, CCIA, Europe's technology and security policy manager, quote, the proposal does not set the technical security or accreditation standards for Kids Act implementation. In other words, it's just sort of like a wish list. So how do you implement a wish list? He said the commission is kicking those critical decisions down the road to future implementing and delegated acts. Europeans are essentially being
[01:18:28] [SPEAKER_01] asked to trust a system before anyone knows how it's actually going to be built. Right. Digital freedoms advocates said the proposal is dangerous and imperils the privacy of all Europeans. Simone D. Brouwer, policy advisor at European Digital Rights, you know, EDI or EDI or EDI, we've talked about them before, Europe's largest network of digital rights organizations said, quote,
[01:18:58] [SPEAKER_01] if the EU really wants to protect children, it should make platforms prove that they're safe, not make children and everyone else prove that they're old enough to exercise their fundamental rights online. Because the Kids Act mandates all users' ages be verified, when they create social media accounts, adults will also have to submit ID documents. Mobile devices are required to use the EU age verification
[01:19:27] [SPEAKER_01] app and European ID wallets. Debrouwer said the requirement will be particularly harmful for marginalized people who don't have IDs and will strip kids of their rights. And finally, the European Commission included poll numbers showing strong support for more aggressive kids online safety laws in its press release, saying that the social euro barometer on the digital decade 2026
[01:19:57] [SPEAKER_01] survey found that 92% of Europeans consider better kids online safety protections a top policy priority. Yes, we would like you to help protect our kids, but please do it in a sane fashion, not this mess, which is, you know, destined to go wrong. So that reporting by the record mentioned the European Commission's official open source age
[01:20:26] [SPEAKER_01] verification app, which was released earlier this year in April. Sadly, it was deeply flawed from the start. It was readily bypassed, get this, Leo, by editing local config files. The PIN was not cryptographically tied to the credential store, so PIN entries could be deleted. A new PIN could be set, and the original profile's credentials
[01:20:56] [SPEAKER_01] could be reused by other people. So, I mean, there was like no protection. Believe it or not, the brute force retry prevention counter was stored as an editable value, which could be reset. So you reset the brute force retry counter whenever you want to. And the requirement for biometric agreement could also be turned off because it was a simple true
[01:21:26] [SPEAKER_01] false setting in the config file. It wasn't safe against token replay. So, one researcher created a Chrome extension that captured and replayed the same I'm over 18 token over and over to any websites that asked for it. And even if all of that was already enough of a disaster, the architecture of the entire system is such that the token issuer serves as
[01:21:55] [SPEAKER_01] a gatekeeper that's able to log when and where every credential they issue is used. So, I mean, it's a disaster in every form and fashion. You know, and of course, a solution is right in front of us, but no one appears to be stepping up because everyone has their own agendas. For the past several years, we've been watching Apple with iOS and Google with Android
[01:22:25] [SPEAKER_01] reluctantly providing their own devices, local age assurance systems, as they've been necessitated by app store access laws that have been passed in Utah, Texas, Louisiana, as well as Brazil, Australia, and elsewhere. So, those systems are in place now, right? I mean, Apple has this. Apple calls theirs their declared age range API, which we've talked about extensively before, and Google's
[01:22:54] [SPEAKER_01] is the Play Age Signals API. So, any and all native social media applications running on either Apple or Android platforms are already able, right now, today, to determine their users' declared ages and alter their operation accordingly to whatever degree they choose. What's missing is the link to websites. Any web
[01:23:24] [SPEAKER_01] browser running on either of those platforms can also determine the age of their user from either platform's native API. That's in place. But there's no existing mechanism for offering that declared age to a website. Since September of last year, so here we are in September of 2026, in September 2025, Safari and the various Chromium-based browsers have
[01:23:54] [SPEAKER_01] been able to request a W3C-style digital credential which would have been stored in the device's wallet. But, for anonymity and privacy, only the user's age range should be provided, yet there's no provision for that. This means that we have, right now, everything we need to allow a user device to assert the privacy
[01:24:24] [SPEAKER_01] enforced age range of its user, not only to local apps, which we already have, and the app stores, but to websites. But, unfortunately, the necessary parties have not agreed to get that done. And it certainly appears that the European Commission is still a long way from having anything that is even barely acceptable as a privacy enforcing solution. I just, you know,
[01:24:54] [SPEAKER_01] I guess they passed this legislation, Leo, because 92% of their citizens said in a poll that we would like something. So, they just gave them a stew of, you know, a wish list of nothing that doesn't provide anything that is rigid enough that anyone could implement something to. do. And so, nothing is going to happen. Yet, here they are, you know, trying yet again.
[01:25:26] [SPEAKER_01] Okay. The prolific pain in Microsoft's butt hacker who uses the handle Nightmare Eclipse and sometimes goes by Chaotic Eclipse, whom we've talked about, well, pretty much nearly every month for most of 2026 because of all of the zero days that were released on Patch Tuesday, right? All of those, voluntarily
[01:25:56] [SPEAKER_01] outed himself last week. Yep. Via a posting on X in a thread titled Storytime, his given name is Abdel Hamid Nasiri. And the last name Nasiri rings a bell for me. I mean, I think we saw some things from a Nasiri at Microsoft like sometime last year. The name really connects for me and I don't
[01:26:26] [SPEAKER_01] know why otherwise it would. He is a former Microsoft security researcher based in Germany. An X poster who posts under International Cyber Digest says that they've known this person for some time and so confirmed what was said. In their own posting on X, this International Cyber Digest wrote, Nightmare Eclipse,
[01:26:55] [SPEAKER_01] the person who's been dropping Windows zero days, has finally decided to share his story. He's an ex-Microsoft employee. We had dinner together and I've known him, writes this person and his story for some time. His real name is Abdelhamid Nasiri. He's a very talented and intelligent individual and he came across as someone who'd be a real professional to work with. Quoting
[01:27:25] [SPEAKER_01] Nasiri, quote, if only I didn't pour my soul into that job with countless of stupid non-sleep nights, I would have gotten over it. Dot, dot, dot, unquote. Okay. International Cyber Digest writes, he loved Microsoft. I wouldn't say that what he did, releasing all those zero days, was normal, but he felt he had no other option
[01:27:54] [SPEAKER_01] because of the injustice Microsoft did to him. They fired him and you can read the vague reason they gave in the email sent to him by the Vice President of Engineering at MSRC. According to Abdel's account, VP Tom Gallagher met with him after the firing to tell him they were blacklisting him from Microsoft and writing him a bad reference so he'd never be able to get a job again. Normally,
[01:28:24] [SPEAKER_01] you'd think, well, big deal, just find another job, right? But Abdel doesn't have a European passport and he was only a couple of months away from getting permanent EU residence. So instead of granting him those couple of months, Microsoft fired him for a reason that as far as we can tell was never made clear, then fought him in court and offered him 55,000 euros plus a year's pay to drop
[01:28:54] [SPEAKER_01] the case, which Abdel brought against Microsoft, by the way, all while Abdel was releasing zero days. Abdel continued suing Microsoft for unfair termination in Germany, a fight that has cost him over $200,000. He says Microsoft refused to reveal any details about the security breach and went another direction. If you are reading this and you can
[01:29:23] [SPEAKER_01] offer him a legal job, this is his email, msnightmare at proton.me. to which I would reply, if you have read that and you do offer this criminal a legal job, you will deserve what you will likely get. I wouldn't get near this guy with a 10-foot pole. I well understand the bond of
[01:29:53] [SPEAKER_01] friendship that the person posting as International Cyber Digest might feel toward his friend Abdel Hamid, whom he says he's known for some time, but characterizing Abdel Hamid's punitive release of a series of highly damaging zero-day exploits, all of which primarily inflicted damage upon the users of Microsoft's products as not normal
[01:30:23] [SPEAKER_01] behavior by someone involved in an ongoing employment dispute with a former employer would cause me to question this poster's judgment in addition to Abdel Hamid's. Abdel Hamid, who we know as Nightmare Eclipse, is clearly a talented hacker, but he appears to lack any moral or ethical compass. He did something, no one is saying what exactly,
[01:30:52] [SPEAKER_01] that caused Microsoft to decide, as any responsible company would, to put as much distance between him and themselves as they could. And after that, all of his subsequent malicious actions through month after month of zero-day exploit releases on each patch Tuesday, which were deliberately timed to inflict maximum damage upon Microsoft's customers, would have only served
[01:31:22] [SPEAKER_01] to confirm to Microsoft that they did the right thing by cutting this individual loose. You know, being an extremely talented hacker who's demonstrated his willingness to deliberately attack and damage others will likely bring him to the attention to the attention of other needy criminal gangs. And now they have his email address. But I'd be surprised if any legitimate company would feel differently toward him than Microsoft did.
[01:31:51] [SPEAKER_01] It is a shame to see such talent used to hurt others, and it's a shame that such a talented hacker, you know, has decided to abuse his own talents this way. But, you know, now we know the story. We do have a snippet of the email that this VP Tom Gallagher sent. And it's interesting, Tom referred to him by his last name,
[01:32:21] [SPEAKER_01] saying, Hi, Nasiri. Thank you again for meeting with me yesterday. I appreciate that you wanted to better understand the company's concerns. What I can share with you is that the company identified a potential security breach. Our security team raised concerns that you put the company and customers at risk by sharing vulnerability information with external parties. This credible
[01:32:51] [SPEAKER_01] escalation has caused me to lose trust in you and why we spoke earlier about a mutual separation. As explained, Christina from HR has sent you a proposal of a termination agreement. Please review it carefully and let me know within one week if you will accept it or not. So reading between the lines, and there's been a lot of coverage of this in the tech press, it looks like what happened
[01:33:20] [SPEAKER_01] is that nightmare eclipse disclosed something to some third party. that is he was talking out of school about Microsoft software and it got back to Microsoft and I was like sorry, you can't stay here. You can't have access to our source code tree any longer. You need to go. And he brought a suit against them and refused
[01:33:49] [SPEAKER_01] to settle after multiple attempts by Microsoft. giving him 55,000 euro plus a year's pay to drop his suit and he said no. In other reporting I saw, he now regards his suing Microsoft as having been a mistake, but that was the decision he made at the time. Anyway, it's a sad situation, but these things
[01:34:19] [SPEAKER_01] happen. He's no longer at Microsoft. I imagine again, I will be surprised if any credible company would hire this person. You just can't. How could you? I mean, I would argue a company would put themselves at risk if knowing what they know of him, they were to hire him.
[01:34:39] [SPEAKER_00] And now especially. I mean, he's kind of doubled down on the whole thing. Unfortunately.
[01:34:45] [SPEAKER_01] I sue somebody who terminates me and sorry, there are plenty of people who are available for hire right now. So he's not going to be at the top of the list.
[01:35:00] [SPEAKER_00] These things happen. I am reminded of our friend Randall Schwartz, who's a legendary Pearl programmer and great guy who used to host our Floss Weekly show, who got in trouble at Intel because he found a security flaw and he said he was pen testing, but it was in a different department and he used the security flaw to break in. And not only did Intel get him in trouble, he got arrested for it. And I think he did it with the best intention.
[01:35:30] [SPEAKER_00] But you know, sometimes we geeks don't really read the room very well. Doesn't he have a felony conviction now? I believe so. Yeah. Yeah. Yeah. And I, and honestly, I don't, I don't believe he was being malicious or attempting to hack until in any way he thought he was helping them discover a vulnerability, but it didn't, you know, the company didn't take well to it. And, uh, and I understand how we, and we
[01:35:59] [SPEAKER_01] talked about this on the podcast about how can a hacker who does discover a vulnerability responsibly and protect himself. Yes. Protect himself from a backlash by the company because certainly years ago when we were talking about this, companies were suing the people who were, who had hacked them, but then said, oh, well, yes, I hacked you, but you need to fix this. You know, CEOs, you know, told their attorneys, go sue this kid.
[01:36:29] [SPEAKER_00] Right. Right. It's, it's a sad story all around,
[01:36:35] [SPEAKER_01] I guess. And you're right. We don't Randall. There's no way that Randall was, was malicious. No, he said he's a sweetheart,
[01:36:41] [SPEAKER_00] but he, you know, he, I think a lot of us are a little on the spectrum and I think he just didn't read the room. I remember when we went on a geek cruise, he came up to me and whispered in my ear, he said, your email password is I said, what? And he said, well, you're sending it in the clear on the, on the wifi network. And he was right to tell me the execution lacked a little bit and I could see how some people might take
[01:37:11] [SPEAKER_00] umbrance and not react well to that. And it's the same, it was the same kind of thing. It's just kind of a tone deafness. Um, that was not ill founded. He, I mean, I was glad he told me, you know, he said, you're sending, you know, this is wifi and you're sending it in the clear. This was before HTTPS, I guess. Right. And, uh, and you should know about that. And I think he probably did this to everybody on the geek cruise,
[01:37:35] which is
[01:37:36] [SPEAKER_00] really not the best way to announce it is I'm just, is what I'm saying. That's all. We love
[01:37:41] [SPEAKER_01] him very much. Yeah. What would have been, what would have been better would have been to make a, well, I don't know. I was going to say, make a broad announcement to everyone. Exactly. A generic announcement. Protect yourself. Everybody should know that, you know, we have an unsecured wifi. So email, uh, if, if you're just using standard SMTP to send your, you know, to log in and transact, that's not being protected.
[01:38:08] [SPEAKER_00] You're on the ship's network. Yeah. By the way, uh, uh, Briggs tells conviction was expunged in 2007. So he is in the clear now. Oh, good. Good news. Good, good, good, good. And I'm not revealing any secrets. He talks about it's in his Wikipedia article and he talks about it. Yeah. Yeah.
[01:38:27] [SPEAKER_01] Uh, okay. Let's take a break because we've got two more big topics to talk about and then we will get to
[01:38:32] [SPEAKER_00] our main topic. All right. You're watching security now with the one and only Steve Gibson, who has, to my knowledge, never hacked any of our servers. Not that he couldn't, but he doesn't have no interest. That's really more of it. I have other things to do. I think when you were a teenager, you probably maybe got
[01:38:53] [SPEAKER_01] I had the grand master key to the every door in the district of San Mateo Union High School district. So yeah, they could have taken that the
[01:39:03] [SPEAKER_00] wrong way. I think it's pretty much the case that every single person of our vintage was hacking in the early days in some form or fashion, right? I used to go through the hex code on games to delete, to eliminate the copy protection so I could make copies of the game floppy, things like
[01:39:25] [SPEAKER_01] that. I've removed my share of protection from things that I bought and then the company went out of business and I couldn't use it anymore. Yeah. And by the
[01:39:35] [SPEAKER_00] way, that's how I, and I bet you too, learned hex, learned how to read hex as well as plain English. I'm they brought to you by Threat Locker. Threat actors these days, they're not like me and Steve. They are bad guys. They are using AI to automate vulnerability discovery, to modify scripts during an attack. It's so fast that you can actually adjust the attack as you're in the
[01:40:05] [SPEAKER_00] middle of it. They're using AI to generate new malware variants, to coordinate activity across multiple systems. It gives them the chance to attack many hundreds of systems at the same time. And it does it all at lightning speed, which means that tasks that once took an individual hours or days to achieve can now happen in seconds. And that is scary for us. You know, the people have to defend these systems. And sometimes as Steve said, the cult's coming from
[01:40:35] [SPEAKER_00] inside the house. Organizations are adding AI assistants and agents and without a lot of governance, they can access documents, source code, cloud applications, API, internal systems. If you're on the security team, all of that should give you a nightmare, right? You need to know what's going on here, what AI tools are in use, what information they can access, whether they're operating inside or outside their intended scope. And you don't get a lot of evidence, you know, a successful log in, maybe a, oh,
[01:41:05] [SPEAKER_00] that's an unfamiliar file hash. That's not going to give you enough context. Teams also need to understand whether an application is behaving normally, accessing unexpected data, or communicating with systems it should not reach, like hugging face. You need to know that, right? You want to know that. Well, here's the easiest way to know it, ThreatLocker. ThreatLocker is so genius. In fact, I've talked to people who got the ThreatLocker demo, you can try it for a month, and immediately
[01:41:35] [SPEAKER_00] saw stuff they never knew was going on in their network, remote access tools, dozens of them that were being used by employees without their knowledge, just things like that. ThreatLocker uses a variety of techniques to protect you, application allow listing, much more than ACLs. We're talking you control which AI, various tools, and other applications are allowed to run. They have ring fencing, that's their term for zero trust. They use ring
[01:42:04] [SPEAKER_00] fencing to limit what approved applications can access, which processes they can launch, how they communicate. This is new, web content control, which manages access to public AI platforms and other online services. So they've extended zero trust from endpoints to company networks, network applications. You've got privileged access management, which prevents AI applications and their users from receiving unnecessary administrative privileges, privilege escalation.
[01:42:34] [SPEAKER_00] ThreatLocker applies zero trust network access, zero trust cloud access policies, and of course endpoint access policies to restrict resources to the authorized users, to the approved devices, to the permitted applications. And it works on everything, Windows, Mac, and Linux. They have the best US-based support, engineer to engineer, 24-7. And that's why ThreatLocker, because they're so good, they're trusted by organizations that cannot afford to go down for even one millisecond. Companies
[01:43:04] [SPEAKER_00] like JetBlue uses ThreatLocker. Heathrow Airport, they've learned their lesson. They are very careful. Indianapolis Colts, infrastructure, like the Port of Vancouver, they use ThreatLocker to stay safe. Asked Jack Thompson, he's director of information security risk and compliance for the Indianapolis Colts, he said, quote, with ThreatLocker, we have the ability to centralize disparate elements in the security stack, end quote. And I'll complete that thought because when you
[01:43:33] [SPEAKER_00] centralize it, it gives you visibility. Now you can see, and this is what really is lacking. You don't know what's going on inside your network. ThreatLocker gives you that visibility. ThreatLocker has also, of course, received the top marks in industry recognition. January 2026, recognized a strong performer that was in the Gartner Peer Insights voice of the customer. that was for endpoint protection platforms. They were ranked number one in application control by Peerspot, won the
[01:44:03] [SPEAKER_00] best zero trust security solution at the 2025 TICE awards. And I can go on and on. You'll find it all at the website, threatlocker.com slash twit. AI governance requires more than an acceptable use policy. It's not, yeah, you have the policy, but do you have the protection? ThreatLocker gives security teams the technical controls to define which AI tools are approved, who and what can access them, and how those tools are allowed to interact with business systems and data. And that's just a part of what ThreatLocker does. Visit
[01:44:33] [SPEAKER_00] threatlocker.com slash twit, get that free 30-day trial, and learn more about how ThreatLocker can help mitigate unknown threats and ensure compliance. That's threatlocker.com slash twit. They really are the best. You're muted. It's not me. Did I mute you? No.
[01:44:57] [SPEAKER_01] You muted you. Sorry, I did. So apropos of our last conversation, where we were just talking about people hacking in other companies, we've covered many instances where, because it's been what's happening, where agentic AI got loose, broke out of its containment, and was later discovered to have behaved badly. Or we would now say to have behaved in a misaligned fashion.
[01:45:27] [SPEAKER_01] That's right. But what about a security firm using AI to proactively, deliberately, and successfully attack another firm's security? Not a mistake, but, you know, deliberate. When an exploitable vulnerability is found not using AI, in other words, the old-fashioned way, you know, we award those industrious hackers with a bounty.
[01:45:57] [SPEAKER_01] And this makes the Hacker News headline from last Saturday all the more intriguing. Their headline was, Claude Opus 5 helped researchers take over open AI staff accounts via chained flaws. flaws. And there's a lot of meat in this. There's a lot for us to talk about here. So here's what the Hacker News reported. They said three researchers at the security firm Hacktron, you gotta love
[01:46:27] [SPEAKER_01] that. So it's, you know, sort of suggests maybe automated hacking, and that's exactly what it is. From the security firm Hacktron, used Anthropics Claude Opus 5 to chain two flaws and take over the chat GPT and codex accounts of several open AI employees, then reach an internal open AI code repository. In other words, a total breach of
[01:46:57] [SPEAKER_01] open AI security leading to full access to open AI's proprietary internal code repository. Yikes. The Hacker News continues writing, the chain began with a bug in the software that runs open AI's public help forum and moved through research not a real world attack. The team
[01:47:26] [SPEAKER_01] reported the flaws to open AI, proved their access with a deliberately harmless pull request, then stopped. From the first look they made, obtaining that full internal access took under 72 hours. Open AI confirmed a fix about 14 hours after the report according to Hacktron and on September
[01:47:56] [SPEAKER_01] 1st paid the team a $6,500 bounty. Open AI said the award recognizes the open AI side finding not the actions against discourse which is the open source software that runs the forum. Testing the forum itself was
[01:48:16] [SPEAKER_00] out
[01:48:18] [SPEAKER_01] testing the forum itself was out it turns out it was an image display bug but we'll get there in a second testing the forum itself was outside its bug bounty program right because that's you know open AI is only talking about their side of it they said open AI has not publicly described the login flaw and it confirmed the finding through that fix and payment rather than by detailing the account takeovers hacktron
[01:48:47] [SPEAKER_01] which describes itself as an AI assisted security research firm was careful about what it did and did not do when one employee's codex link to open AI code on github was opened it triggered a single pull request in the internal repository it did not read any source code merge ship anything or touch customer data what the chain could have
[01:49:19] [SPEAKER_01] reached they wrote was far larger because staff connects other services to chat GPT and codex
[01:49:57] [SPEAKER_01] the sign in with open AI option the same single sign on that staff uses elsewhere so thus a collision in single sign on overlap the article said once the researchers took control of the forum server the shared login let them take over the chat GPT and codex accounts
[01:50:51] [SPEAKER_01] and discourse passes uploaded heic and heif often verbalized as heif images to a tool called image magic very popular image rendering tool which uses the live heif library to read them a flaw in live heif let a specially crafted image corrupt the
[01:51:21] [SPEAKER_01] forum server's memory now here's where it gets cool leo discourse as advisory rates the result as remote code execution scores at 8.8 out of 10 and tracks it as cve no 2026 32 882 so discourse should be updated everybody in order to get rid of this live heif exploit which is now known publicly the public record for the
[01:51:51] [SPEAKER_01] flaw itself is narrower in live heif's own advisory and in national vulnerability databases that cve ending in 32 882 is an out of bounds read that can crash the software or leak nearby memory not a direct code execution bug here we go that leaked memory helps defeat a common protection called address space layout randomization
[01:52:21] [SPEAKER_01] the researchers say they combined live heif's memory bugs with the AI's help to turn the crash into working code execution on the forum server upstream the flaw was fixed in live heif 1.22.0 in May of 2026 so everyone will want to make sure that they're running an instance of image magic that
[01:52:51] [SPEAKER_01] incorporates live heif with 1.22.0 which would have been sometime in May that fixed existing month that fix existed which is interesting months before the test but the forum's server image built on the debian 12 linux distribution still shipped the old unpatched live heif
[01:53:20] [SPEAKER_01] version 1.19.7 when the researchers looked in July the fix and its CVE were already public but debian had not yet included them in the packaged version the forum used if you run your own discourse server this part affects you directly they wrote rebuild on the latest image to get the patched live heif because a web interface update alone may
[01:53:50] [SPEAKER_01] not replace the old library sites hosted by discourse were already patched and the fixed self hosted releases are 2026.7.0 .6.1 .5.2 and .1.6 so how did the researchers use AI they used AI to do the hard part they first tried Claude
[01:54:20] [SPEAKER_01] Opus 4.8 which struggled over several sessions to build a working exploit once ASLR was enabled I'll have a lot to say about this in a minute Anthropic released its next model Claude Opus 5 on the evening of July 24th and in a fresh session it produced a working code exploit within hours wow
[01:54:49] [SPEAKER_01] so here we have Opus 4.8 can't do it no matter how many times they try Anthropic updates Claude to Opus 5 bang cuts through it like butter they said Opus 5 shipped with safeguards here comes more Opus 5 shipped with safeguards meant to stop it from writing exploit code for real targets which it did the
[01:55:18] [SPEAKER_01] researchers got around them by pointing the model at their own test server disguised as a capture the flag practice target then letting it run in an automated loop even so they say the work was not hands off skilled human direction still mattered and this was not automated hacking with no one at the controls the case fits what researchers and AI companies have described this year capable
[01:55:48] [SPEAKER_01] AI models are sharply cutting the time and skill that serious offensive work used to require Anthropic has reported that criminal and state backed groups are already using its cloud models to run real intrusions not just to ask questions or rather ask and answer questions open AI was one target in a wider project hack Tron calls
[01:56:18] [SPEAKER_01] he heist over about two months the team says it found the image decoding flaws in software used by other large companies right because everyone's using this at a total cost of under $3,000 in their AI usage it links the campaign to reported bugs in Slack Meta's products github enterprise and web frameworks
[01:56:48] [SPEAKER_01] such as next JS those broader claims are backed unevenly the next JS flaw is confirmed in Vercel's own advisory and live heath's maintainers confirmed a working code execution exploit for the bug tied to meta the wider claim of code execution across many applications has first covered the next JS flaw in August
[01:57:17] [SPEAKER_01] the wider campaign used a different model open AI own GPT 5.6 SOL for cases where the team knew nothing about the target in advance only one company Shopify appears to have noticed the activity the researchers say even though its image processors crashed repeatedly under thousands of test uploads in other words many companies don't notice that somebody is
[01:57:46] [SPEAKER_01] hacking their systems only Shopify said hey what the hell is going on here most companies were completely oblivious to it again that's a problem the hacker news has contacted haktron with questions about how the forum code execution was achieved and about the scope of the account access so what should users do the bigger lessons go beyond discourse if your service accepts user images and reads
[01:58:16] [SPEAKER_01] heic heif or avif files through live heif an old build could be exposed and if a public lower trust service shares your single sign-on with internal tools which was the mistake open ai had a break in on that service can become a break in everywhere which the same login reaches update live heif to the latest security release
[01:58:45] [SPEAKER_01] 1.23.4 as of early september 2026 or to your distributions patched build where you do not need it turn off decoding of untrusted heif and avif images or run image processing inside a lockdown sandbox limit which services your single sign-on trusts and require a fresh identity check before sensitive actions rather than trusting an existing session
[01:59:15] [SPEAKER_01] again it's that common session reuse problem is where this bit open ai they finish there's no sign the open ai flaw was used against anyone in the real world as of mid september 2026 it was not on the u.s government's list of vulnerabilities known to be exploited you know cissa's kiv although that list is not proof either way what the available reports do not settle is
[01:59:44] [SPEAKER_01] whether an organization that has already patched should still check for earlier access on that point all sources are silent okay so we learned a number of very interesting things from this reporting it was i think really interesting as i said that whereas claud opus 4.8 worked and worked but was unable to develop an exploit simply upgrading to claud opus 5 handed
[02:00:14] [SPEAKER_01] the would-be attackers a working exploit within hours this pretty clearly demonstrates the rapidly evolving effective strength of available ai the next chilling aspect revealed by this report is the successful ease with which the attackers were able to trick both claud opus 4.8 and 5 into bypassing their own guardrails to
[02:00:44] [SPEAKER_01] develop a working exploit for them they used essentially the oh claud it's okay we're a cyber security firm and we're just live heave library could be weaponized in the presence of aslr so we just need you to try to do that for us on our own internal test server would you do
[02:01:14] [SPEAKER_01] that for us pretty please as i've said from the start today's ai technology has always felt very slippery and extremely difficult to control and finally the most worrisome evidence we obtain from this is that the work that claud opus 5 performed for these researchers was truly significant just to remind everyone address
[02:01:43] [SPEAKER_01] space layout randomization ASLR was added to systems as a mean of thwarting attackers who managed to obtain execution inside a protected code space such as an operating system kernel before address space layout randomization was added a system would always load its many various modules essentially stacking them
[02:02:13] [SPEAKER_01] in the same order inside the operating system's RAM memory this meant that an attacker could count on what was located where when they wished to use for example return oriented programming ROP to knit together the privileged changes they needed to make by using the operating system's own existing code at the ends of existing subroutines
[02:02:43] [SPEAKER_01] they would jump near the end of a known subroutine that would do a little something that they needed before it returned and when it returned it returned to them being a subroutine so ASLR was added to make doing this far far more difficult as the name says address space layout randomization deliberately does not load all of the system's
[02:03:12] [SPEAKER_01] modules the same way each time in fact it goes to extreme lengths to scramble up the loading so that no code an attacker might manage to get running inside an operating system kernel will have any idea where anything else is located ASLR consequently has proven to be an extremely effective and essentially critical attack success mitigation technique
[02:03:42] [SPEAKER_01] the technique is so difficult to bypass that Claude Opus 4.8 was unable to succeed it stopped at cold but then along comes Claude Opus 5 which reportedly cut right through ASLR understand how bad that is ASLR bypasses have been known in the past because it is at best
[02:04:12] [SPEAKER_01] a mitigation a strong mitigation but still just a mitigation it is not never has been and cannot be a total prevention it makes the attacker's job far more difficult but it is unable to make it impossible until now ASLR has meant that only the upper echelon of elite hackers you know these
[02:04:42] [SPEAKER_01] hacktron people couldn't only the upper echelon of elite hackers could find their way past it Claude opus 5 just changed that now all any script kitty needs to do is ask for passage no elite hacking skill required so I'm very glad that there are now white hat hacking firms like hacktron which have decided to
[02:05:11] [SPEAKER_01] leverage the power of AI to find and report remotely exploitable vulnerabilities and collect bounties that's great we need more groups like them it would be terrific if they could be granted fully cyber capable access to anthropics best models without guardrails so they don't need to try trick claude to do what they would want to do in order to protect firms from themselves
[02:05:41] [SPEAKER_01] these are the sorts of people that we want to up arm in what is going to be something of a cyber war here for a while i
[02:05:50] [SPEAKER_00] like that verb uparm that's new to me
[02:05:55] good get
[02:05:59] [SPEAKER_01] prepared arm your up also last Thursday the hacker news carried the report of a maximum severity and you never want to read this about something that cisco is offering a maximum severity cvss 10.0 which we know is incredibly difficult to get i mean basically if you have a vulnerability of 10.0 the device is saying come on come on in just you know
[02:06:28] [SPEAKER_01] come in look around take over my enterprise that purchased me it is remotely exploitable to give anyone who wishes root access and full control over an affected cisco device starting off the article the hacker news wrote cisco has warned of a fresh maximum severity security flaw impacting identity
[02:06:58] [SPEAKER_01] services engine is that has come under active exploitation so the word is out the vulnerability tracked is cve you know 2026 76 460 with a cvss of 10.0 could allow and we know now does is does and will allow any unauthenticated remote attacker to bypass
[02:07:27] [SPEAKER_01] authentication cisco wrote this vulnerability is due to insufficient authentication control which yeah no kidding on an api endpoint an attacker could exploit this vulnerability by sending a crafted request to an affected api endpoint a successful exploit could allow the attacker to gain unauthorized access
[02:07:57] [SPEAKER_01] to the affected device by bypassing the web based management interface well our listeners well know how much disdain i have for any and all publicly exposed web interfaces it's almost to the point now where you deserve what you get if you expose a web interface all of the evidence we've seen for years proves beyond any doubt that for whatever reason we just do not
[02:08:26] [SPEAKER_01] seem to know how to secure a web interface we just don't we can't apparently if these problems directly damage cisco they might have removed those inherently insecure interfaces long ago but since cisco's users want them and since it's they who are damaged by the endless ransomware extortion campaigns they enable nothing ever changes
[02:08:56] [SPEAKER_01] even when cisco comes under hopeful new management as we covered last year sometime that promises to put their customers security ahead even ahead of the customer's own convenience well that doesn't seem to change what has changed for the better is that as i said at the top of the show cisco like microsoft has apparently also discovered that ai can help them
[02:09:25] [SPEAKER_01] to finally root out these latent legacy problems last wednesday the day before uh that reporting uh cisco dropped what is for them a stunning ensemble of 77 patches for systems across their product line i'm not going to go through it all but i'll give you a sense for it we've got all of cves are of course
[02:09:55] [SPEAKER_01] 2026 so 2176 has a cvss of 9.9 2211 9.1 2307 9.1 all multiple vulnerabilities in that isc that could allow an authenticated an authenticated remote attacker to execute arbitrary commands on the underlying operating system of an affected device to exploit these
[02:10:24] [SPEAKER_01] vulnerabilities the attacker must have valid admin credentials unfortunately if you have that you can just take over the device do whatever you want to outside of normal controls then we have 76462 carrying a cvss of 10.0 76464 425 426 427 428 multiple vulnerabilities in isc
[02:10:54] [SPEAKER_01] and cisco isc passive identity connector known as isc pic that could allow and we now know does a remote attacker to bypass authentication to the rest api achieve remote code execution perform sql injection and conduct mxl external entity injection attacks on an infected device cve 20 282 with cvss of
[02:11:50] [SPEAKER_01] cvss 9.1 cve cve cve 326 cvss of 9.8 2360 361 76409 multiple vulnerabilities in cisco nexus dashboard that could lead to command injection authentication or authorization bypass and information disclosure cve 2130 with a cvss of 10.0 20
[02:12:20] [SPEAKER_01] 192 cvss of 10.0 21 94 a cvss of 9.1 then another 9.9 and 9.9 multiple vulnerabilities and isc blah blah and it goes on like that for a total of 77 and they are all in the high nines of cvss scores we don't have to guess where these all came from right we see the pattern that the employees
[02:12:49] [SPEAKER_01] of massive legacy enterprises Microsoft and cisco come to mind the employees are unable to clean up their own legacy code but as i said at the top when those cash rich enterprises can pay to have ai do that for them their code gets fixed and that is nothing but really great
[02:13:19] [SPEAKER_01] news so at this rate you know as with microsoft cisco's platforms may at least finally become securable which would be wonderful what is i mean they're everywhere right
[02:13:36] [SPEAKER_00] there oh
[02:13:37] [SPEAKER_01] my god yes cisco was first and there they've always been like the ibm right like you can't go wrong by ordering cisco and which is you know it's been the bane of many of their competitors who have said uh you know their their stuff is not that great anymore look at what we have but people like
[02:14:01] [SPEAKER_00] well it's you know in their defense and microsoft's defense when you've been around forever and ever your code base gets a little old and grungy and you know but this is good we're getting this stuff fixed up now
[02:14:12] [SPEAKER_01] yes i salute them if you cannot hire people to fix your legacy code and apparently microsoft and cisco can't then hire ai to do it and it is doing it i mean this is uh external exposure vulnerabilities in cisco what it does mean is you got to get your gear updated because the bad guys are going to backtrack these vulnerabilities
[02:14:42] [SPEAKER_01] and attack you with them so really really really update cisco if if any of our listeners have any responsibility for cisco gear on the edge make sure that it's uh it's updated and leo it's time for our last our last break and then we're going to take a look at speaking of a super rich company that uh is spending a lot on ai to fix their problems it turns out it's not all good news
[02:15:12] [SPEAKER_01] the mega patch tuesday fallout is our final topic there was a little bit yes well we'll talk about this good
[02:15:19] [SPEAKER_00] okay
[02:15:20] [SPEAKER_01] more than you know oh yeah really bad
[02:15:25] [SPEAKER_00] well you know that's why people come here they want to hear the bad news with the good news in fact it's mostly bad news but if you are responsible for keeping your company's systems running or protecting your security this is the news you need to know right this episode of security now brought to you by out systems i love out systems the leading agentic systems platform let me explain what this is all about out systems is uh is helping their
[02:15:54] [SPEAKER_00] customers modernize operations operations by enabling their customers to build modernize and operate enterprise systems starting from any coding tool in a very important these words listen carefully governed i'm underscoring that one agentic engineering model all right it's time to innovate at the speed of ai we all want to do that but we also i hope do not want to compromise quality or lose control
[02:16:23] [SPEAKER_00] which is why so many thousands of enterprises worldwide trust out systems for their mission critical apps i mean we're not this is not theory this is not just a good idea we're talking about massive operational wins take for example a leading global retailer you would know the name that was struggling to keep up with their rapid expansion they turned out systems to build ai agents that automated their invoicing and translation processes
[02:16:52] [SPEAKER_00] shifting 95% of their daily store operations to a new digital app saving thousands of hours of manual work and i'll say this parenthetically when you have when you build an agentic workflow that is constrained that is specific that works with a specific kind of data set it becomes so reliable so useful that you can really trust it and that's what our system specializes in or take a look at the major
[02:17:22] [SPEAKER_00] global logistics giant that was drowning in technical debt i think any company that's more than a couple of years old is probably their engineers are spending most of their time weeks manually firefighting by reviewing platform logs sound familiar by using out systems they were able to build an ai log review agent in just five days and that one agent just that one agent now saves them over 1600 engineering hours every single
[02:17:52] [SPEAKER_00] year that means their team can focus on real innovation instead of you know reactive maintenance even in modern digital banking and banking is challenging right because there are a lot of regulations a lot of restrictions there's a high demand for security and reliability but yes even in banking companies are using out systems to standardize and automate complex financial workflows delivering secure personalized experiences at a pace their competitors can't match
[02:18:22] [SPEAKER_00] because it's out systems it's reliable it's secure it's robust out systems gives you the flexibility to deploy how you want and the governance to do it safely so stop chasing the hype and start building systems that actually scale learn more at out systems dot com slash twit that's out systems dot com slash twit if you've only taken away one thing from today's show let it be this out systems dot com slash twit this is the solution you're looking for
[02:18:52] [SPEAKER_00] we thank him so much for supporting steve and security now mega okay so
[02:18:59] [SPEAKER_01] last week we noted uh that while it was super spiffy terrific that microsoft has now leveraged ai to fix things left and right within each month breaking all previous historic records there was also some consequential downside in the form of the massive burden that all of these patches would have on enterprise it staff who
[02:19:29] [SPEAKER_01] now needed to make sure that applying these fixes did not break anything that their enterprise might depend upon and despite the need to proceed with caution just days before the release of these patches which was now two weeks ago or three weeks ago microsoft publicly warned their customers to apply these fixes without delay with the argument that ai assisted exploit
[02:19:58] [SPEAKER_01] development was so it was somewhat ironic that it was microsoft as turns out that needed to quickly pivot into emergency mode to address the many widespread catastrophes that were created by tuesday's updates what happened well there's the rdp hang within
[02:20:28] [SPEAKER_01] 48 hours admins began reporting that rds the remote desktop services on patched windows servers would run for a few hours and then die new systems would hang at the connecting dialogue or at the please wait for the remote desktop connection screen and at time of the collapse any existing sessions
[02:20:58] [SPEAKER_01] that were in place were unable to disconnect or log off it was a mess because so many organizations have become quite dependent upon remote desktop which of course Microsoft has been pushing as part of their whole virtualization move but the trouble turns out was not limited to rdp also when this occurred mmc the Microsoft management console are the rds licensing diagnoser even windows file
[02:21:27] [SPEAKER_01] explorer and windows update settings page would all become unresponsive on the affected machine admins were forced to hard reset production servers during the day and the blast radius of this one was pretty significant server 2012 2012 2012 r2 2016 2019 2022 2025 plus windows 10 21 h2 22 h2 and
[02:21:57] [SPEAKER_01] windows 11 24 h2 25 h2 and 26 h1 you know like like frankly the server i'm still running is 2008 it was spared because it was older than they forgot it existed what are you talking that's right although i won't be i'll be up to server 2025 as soon as i bring the new hardware online but i'm not there yet so
[02:22:27] [SPEAKER_01] anyway microsoft's reaction was to offer what is known as a known issue rollback which you know they've had to do in the past which is again this is why enterprise it is a little you know careful with these windows patch tuesdays the known issue rollback could be administered via group policy and then finally on the 14th of september six days after patch tuesday so it
[02:22:57] [SPEAKER_01] was actually it was monday the day before last week's podcast microsoft pushed seven individual out of band updates out to cover all troubled target machines and for the various servers unfortunately on the server side those updates were catalog only so they do not come through windows update and admins were required to get them
[02:23:36] [SPEAKER_01] when again the source of this one was really sort of interesting windows 11 users were prevented from logging in with valid domain credentials after installing the september 26 security updates you know patch tuesday for this month microsoft has been gradually promoting a feature called machine identity isolation it tightens how a machine account
[02:24:05] [SPEAKER_01] goes about proving itself over the net logon secure channel until two days ago I'm sorry until two Tuesdays ago that is before patch Tuesday that feature machine identity isolation had been present but it was set to a configured but not enforced state you know this is sort of the way microsoft creeps these things out and you know microsoft and others where they
[02:24:34] [SPEAKER_01] sort of incrementally roll them out but they don't commit to them it's the way xp originally had a windows firewall it was the first version that had a firewall but it was there but it wasn't enabled by default it wasn't until service pack three I think it was a two or three that turned on the firewall by default anyway so same thing here machine identity isolation configured but not enforced well so you can guess what comes next september's updates
[02:25:04] [SPEAKER_01] flipped it into its configured state with enforcement mode on machines where it had been previously only configured the only problem was that it turns out it's only supported when the domain is at windows server 2025 domain functional level which it turns out is a small minority of the world jeez that's right as a
[02:25:34] [SPEAKER_01] result anyone any enterprises running server 2019 or 2022 domain controllers which again is way the majority most of the world they found that their clients could no longer authenticate to their domains oh yeah
[02:25:53] [SPEAKER_00] that's that kind of puts pasting and excel in the shadows
[02:25:57] [SPEAKER_01] yes it does
[02:25:58] [SPEAKER_00] yes yikes
[02:26:00] [SPEAKER_01] users received the disturbing and clear message the trust relationship between this workstation and the primary domain failed now since cached credentials still work offline users could often log in at home but onto their machine but then find themselves locked out of the corporate network windows credential guard machine account authentication also broke and vpn connected devices
[02:26:29] [SPEAKER_01] were especially prone to trouble because they also use the same trust relationship so it was and still is a mess microsoft has acknowledged the trouble last thursday and offered a work around but not a patch the work around get this is to disable the machine identity isolation feature by enabled it which might be intune group policy
[02:26:59] [SPEAKER_01] or the registry so you set the machine identity isolation value to zero then reboot and then you have to execute a powershell command unfortunately microsoft documentation warns that enabling machine identity isolation in enforcement mode which is what they did which tuesday then subsequently disabling it which is what they are
[02:27:29] [SPEAKER_01] now saying is necessary will break domain authentication and require the device to be unjoined and rejoined to the windows domain i'm sure this was a security feature which they built in you know to be extra safe but that does make recovery more burdensome one solution is to run a powershell command to repair the broken secure channel if anyone out there is being
[02:27:58] [SPEAKER_01] affected by this I got the powershell command in the show notes it's test computer secure channel repair credential and and and get and that will unjoin and rejoin that machine to the domain and then you can log in so you can imagine how many enterprises got bit bit hard by this
[02:28:28] [SPEAKER_01] and took away the lesson it doesn't matter how much Microsoft tells us we need to update this is going to be a problem and then of course we I actually heard from several of our own listeners who are responsible for users within their organization about Excel's copy and paste being broken the update that was responsible was KB 500 2914
[02:28:57] [SPEAKER_01] the good news is that that update resolved 29 different Excel vulnerabilities which included a number of which could be used for serious remote code execution exploits yes so there's that but in the process it also broke our good old copy and paste the thing that caused so much trouble was that the copy and
[02:30:09] [SPEAKER_01] Office 2024 or the LTSC, you know, the long-term servicing channel 2021. They were affected. And of course, since many people spend significant time working in Excel, this was all debilitating for them. You know, not what you want from a Windows patch Tuesday. Then there was USB audio. USB audio class one devices all stopped working with device manager complaining, quote, this device cannot start and giving a code 10.
[02:30:39] [SPEAKER_01] The result was silence. With volume controls unresponsive, the sound settings page sometimes crashing in a related symptom, multi-channel devices lost their eight-channel and 3D audio modes, although stereo kept working. Then there was the WinRE partition to small bugs.
[02:31:01] [SPEAKER_01] The Tuesday update included a secure boot certificate update, which was larger than the previous certificate. That required the need to resize the Windows recovery partition. Unfortunately, systems whose WinRE partition was smaller than Microsoft's recommended 750
[02:31:25] [SPEAKER_01] megabytes, which happens to include an enormous number of OEM images that do not wish to waste so much space because they would rather give it to their users. That would all fail to resize and often then fail to boot. Dell's Optiplex machines were widely reported victims of this. It was a mess. Then there's the code integrity failure.
[02:31:48] [SPEAKER_01] When attempting to boot, HP laptops in particular were hitting a stop code of 0x C043001. code integrity failed to initialize and then receiving a black screen or an infinite restart loop, which because of a secure boot file mismatch. The popular workaround that's been suggested is to disable secure boot in the BIOS.
[02:32:15] [SPEAKER_01] But of course, that means retrieving the system's BitLocker recovery key first. There's all there've also been reports of kernel security check failure boot loops on older hardware. In these cases, it was not possible to simply uninstall the update because the machine would not boot far enough to allow the user to do it. Again, another huge mess. And then there was the Windows Desktop Explorer XE.
[02:32:42] [SPEAKER_01] They like the actual Explorer XE, which is the Windows desktop. It was crashing on any VDI systems, you know, Microsoft's virtual desktop infrastructure. So all the enterprises using Windows VDI through Citrix, UPM, FSLogix, VMware Horizon, Liquidware,
[02:33:06] [SPEAKER_01] Profile Unity, they all virtualized the desktop with remote servers reporting that Windows Explorer desktop failed to start or was crashing immediately after sign-in, leaving a blank screen with no taskbar. A Microsoft engineer confirmed they're investigating and asked for memory dumps, please. But there's no root cause and no fix.
[02:33:30] [SPEAKER_01] The workaround is restarting Explorer from the Windows task manager or just use a fresh profile. But of course, then you've got a whole blank Windows. For an enterprise with thousands of pool desktops, this is another nightmare. And believe it or not, there's more. I'm not going to go into such detail, but AMD Radeon Video, many of their cards suffered black screens, driver timeouts, and hard freezes.
[02:33:59] [SPEAKER_01] There was the BitLocker event ID 24641, which recurred after every reboot. The message that users received was an unexpected error was encountered attempting to retrieve the BitLocker volume master key during restart. Now, that's not what you want to see. However, the drives remained accessible, so it appeared to be some sort of worrisome cosmetic glitch.
[02:34:27] [SPEAKER_01] But it upset lots of people who were wondering what was going on. Hyper-V and Plan 9 shared folders stopped working. Always on VPE with IKE V2 certificate-based VPN. Those connections began failing and dropping immediately. There was a later fix to that using KB5129-195. And finally, update installation failures.
[02:34:55] [SPEAKER_01] Windows 11, LTSC, the long-term servicing channel, 2024, and various Dell notebooks would not accept Windows updates. They would roll them back at the first reboot, and then it was necessary to reinstall them by hand. So I wanted to take the time to walk through these rather than just waving my hand and saying
[02:35:21] [SPEAKER_01] there were lots of problems two weeks ago because it's important to highlight the tight spot this puts enterprise IT staff in and the spot they may be in next month, two weeks from now. Microsoft had said, this is a really important biggie, and due to the new speed of AI-driven attacks, everyone should patch within three days.
[02:35:45] [SPEAKER_01] And this admonishment was offered, as I said, shortly before the delivery of this massive patch update that did, in fact, wreak havoc within the networks of many enterprise users. So what do we do about this? I don't think there's anything we can do. Overall, I think Microsoft did the right thing. Their entire product suite is measurably more secure today than it was two weeks ago.
[02:36:15] [SPEAKER_01] Nearly a thousand patches worth. But they need to learn from this to determine why they did not detect these update side effects. Maybe they were in a big hurry. Maybe junior people are asking AI to fix problems, and they're not vetting them enough. I mean, why were all these things, how did they go undetected?
[02:36:43] [SPEAKER_01] But even if the same thing happens next month, it's unfortunate. And I feel for the enterprise IT guys who are going to be terrified to apply next Tuesday's patches. We don't know how many there are going to be. Only Microsoft knows. And we don't know what quality they're going to be. But I'm afraid we're going to have to go through some pain like this to finally get to a Windows,
[02:37:10] [SPEAKER_01] which not only works for everybody, which, of course, is always the goal, but is also secure.
[02:37:27] [SPEAKER_00] Is that it? I saw you take a drink, and I thought, is he done? Okay. That was a shorter segment than I'm used to. I thought we might go on and on about all the flaws, but there were plenty. God knows. Jeez Louise.
[02:37:45] [SPEAKER_01] There were plenty. And again, I don't know what enterprise does. I mean, they cannot afford to apply these except to do it in their own test environment. They're going to have to test them and see what breaks. But I'm afraid breakage is the way we get there because who knows what next month is going to look like. That's two weeks away, and this is going to happen again.
[02:38:10] [SPEAKER_00] Oh, man. I do not envy the job of our IT professionals who listen to this show. You guys.
[02:38:17] [SPEAKER_01] And you don't want to not patch. No. Because then you could be victim. These are now known flaws. To flaws which are now known. Exactly.
[02:38:25] [SPEAKER_00] They're out there. Yeah. Better to fix them, I guess. The problem is there's such an onslaught. This is what I was saying two weeks ago that Microsoft probably doesn't have time or the ability to test them, not as thoroughly as they'd like.
[02:38:42] [SPEAKER_01] There's probably an urgency on their part to get them shipped. I mean. And unfortunately, when that happens, this happens.
[02:38:50] [SPEAKER_00] A few years ago, I'm going to have to ask Paul about this. Paul and Richard tomorrow in Windows Weekly. A few years ago, they got rid of their testing team, which was maybe a little bit of a mistake. We talked about it here also. Yeah.
[02:39:04] [SPEAKER_01] We'll just let our customers be our beta testers.
[02:39:06] [SPEAKER_00] I mean, right now you need, you want a thousand people. You want somebody on every possible device. You know, you want every computer ever made, every server.
[02:39:18] [SPEAKER_01] You cannot scale that up overnight. And that's what they've had to do.
[02:39:25] [SPEAKER_00] And I think, you know, one of the reasons I kind of laugh when I hear of these doomers talking about how AI is going to kill us all is, and you'll see this when you start playing with local AI. So AI is so smart. It found the flaws, but it didn't find all the side effects. You're so smart. You would think it would have noticed that this is going to break paste. And this has been my experience. They do amazing things, but there are gaps.
[02:39:52] [SPEAKER_00] There are places where they're incredibly stupid.
[02:39:57] [SPEAKER_01] Well, Leo, because they don't actually understand anything. There is no understanding. It is astonishing that just language statistics is able to give us this. It's all it is, is language statistics. We have so much knowledge stored in language that you can, you can query it. You can squeeze it out.
[02:40:18] [SPEAKER_00] But of course it just, it doesn't understand anything. So I'm having the same experience with my own coding. Really very, very careful. I have auditors. I have, you know, some really elaborate checks and balances. And yet, and I mean, I thought, oh, that's really good. The other day I was kind of dejected. I thought, I've got this ad sales system down. Everything's working beautifully. All the numbers work out. It looks beautiful. I said, Lisa, we're ready.
[02:40:47] [SPEAKER_00] I showed it to her. The very first thing she does, it doesn't crash. It says, oh, you can't save that. There's another user. There's no other user. What are you, what are you nuts? It's just us. And it's like, ah, so close. And so it's, it's, it's frustrating because yeah, they, they're not, uh, they're not genius engineers. Even genius engineers make that kind of mistake, but these guys.
[02:41:13] [SPEAKER_01] Well, what we don't yet know is whether AI code slop or to what degree AI code slop is going to be a problem. Are there, you know, I just enumerated the major problems that were created by Microsoft dropping a thousand, nearly a thousand patches. We don't know if there are subtler problems. Like maybe when you, now.
[02:41:39] [SPEAKER_00] We know I guarantee you there are subtler problems. Guarantee you, you know, paste the letter Q into Excel and the whole thing goes, pa-booey. I guarantee you there. Right. Because you can't test everything. Uh, in, it seems to me in theory, I don't know, you're a very accomplished coder. I guess my windows is just too big and office is just too big, but it's very, it's deterministic.
[02:42:05] [SPEAKER_00] You know, where everything is, you don't though wired up and what every, the impact will be of every change you make. It should all be cause and effect.
[02:42:15] [SPEAKER_01] I'm, I'm still of the opinion that we could have a much better coding system because this is just using sample code from the internet to, to knit together solutions. It's, I mean, code is code. It has laws and rules and it's all deterministic. Ultimately.
[02:42:37] [SPEAKER_01] I, I mentioned to you, uh, I think it was before we were recording that all of this has been done with a linguistic model. There are other models now underway. There are world models. There are models for, for, for, for specific areas like, like Microsoft apparently is, is treat, training up a, a, a materials model for some reason. So it won't be language.
[02:43:07] [SPEAKER_01] It'll be something else. And it would be entirely possible to train. I think somehow a code model that is not about language, but is actually about code.
[02:43:21] [SPEAKER_00] You know, there's a new model out there, which you will be able to play with once you get your spark plugged in, uh, called Jev J E V based. It's Jeevon's paradox, you know, and, uh, it's a classifier. It's not an LLM. It doesn't do prose, does new language. And it's very fast and it's very interesting. And I'm actually starting to, I've have about 11 tests going on in different things because it is a very fast and effective way to say this or that. And you give it the criteria.
[02:43:51] [SPEAKER_00] It, it gives you a percentage match and it's really good. And it isn't language.
[02:43:56] [SPEAKER_01] This is, this is that branch that wonders if large language models are not compressors. Um, because, um, uh, G zip is basically a statistical compression. Um, and, and so there, it turns out that you, you can do some, some odd things. It's, uh, it, it, it, it's sort of a branch of what you're talking about. So I, I have sort of run across that, but I haven't played with it.
[02:44:22] [SPEAKER_00] It's very, some very interesting stuff. And because it's so fast, it's very cheap. They don't even charge you for tokens out, just tokens in. And it's, it's really an, we, this is the good news. We're at the very beginning of a revolution.
[02:44:34] [SPEAKER_01] Leo, I, that's what I keep saying is that, yes, that, that this is fun. We are riding a tidal wave and, and nothing we know today is, is true 60 days.
[02:44:46] [SPEAKER_00] Which is why I'm really, really glad, uh, that you got a spark because I want you to start digging deep into this.
[02:44:55] [SPEAKER_01] Uh, I'm very interested in, and well, I want to accelerate my app development because it's dumb that it takes me years to create an app. So I, uh, I I'm the only thing I would ever have it do would be to build, to build my UI, but I spend an awful lot of time moving buttons around and, and tweaking margins and centering things and doing stuff. That's dumb for me to spend time on that.
[02:45:21] [SPEAKER_01] And AI could do very well having a, having a core, my own Masum core in the backend that the, you know, that, that the, and, and a clean interface, uh, API between it and the UI. Then I'm, I'm never, I'm, I will always be using cloud, uh, a agentic cloud coding to code the UI because I would, I'm only going to go for the best. And local is never going to be as good as the cloud.
[02:45:47] [SPEAKER_01] So at least for the foreseeable future, I do foresee a day when Microsoft is offering enterprises an AI server. There, there, there, there will be, you know, you will be able to, you know, there will be a Microsoft AI server. And the other thing that is weird, I shot you a note about it the other day is to remind ourselves that none of this AI is training.
[02:46:12] [SPEAKER_01] I mean, all we're doing is building big prompts around a static AI. It's wrong that an AI that a corporation uses wouldn't learn about like the right things about what the corporation is doing. It's just, you know, built, we're just building really fancy scaffolding around static AI. So we're, we're just at the beginning, you know, baby steps.
[02:46:39] [SPEAKER_00] Well, I'm excited and I'm so glad you're here to guide us through it. Steve Gibson's at grc.com, the Gibson research corporation. That's where you'll find spin, right? The world's best mass storage maintenance, recovery, and performance enhancing utility. It's a must have 6.1, the current version. You can go there and get it. If you already have it, you can get the upgrade for free. He has another program he just put out, which is really cool.
[02:47:06] [SPEAKER_00] The DNS benchmark pro $10 for that. And that will help you find the server for your particular network, which almost certainly is not the one you're using. At least not if you're using your ISP's DNS server. So that's a really nice utility. Very nice tool to have. If you go there, besides those two things, you can also get a copy of the podcast. He has versions in every respect, a 16 kilobit audio version, which is a little scratchy, but is small.
[02:47:36] [SPEAKER_00] That's its primary accomplishment. He also has the 64 kilobit, which sounds fine. Still smaller than the one we offer. And he has the show notes, which are always fantastic. It's like a little mini novel arriving at your desk. 20 pages of stuff. There's pictures. There's all sorts of things you can read along as you listen. And reference road. By the way, they get that as well.
[02:48:04] [SPEAKER_00] Go to the website, grc.com and click the link and download it. By the way, there's also transcribed versions of the show. You can download those for searching as well. Don't mind. Wonderful. But if you want to, you can also do that. You need to go to grc.com slash email. Now, the main purpose of that page is to whitelist your email. Send Steve pictures of the week, ideas, thoughts, questions.
[02:48:34] [SPEAKER_00] So do that. Fill out your email address. He has some magic formula. He'll verify that you're a human without CAPTCHAs, I might add. But there are two little checkboxes below that. One is the show notes. So you can get on that mailing list. The other is a very infrequent new product mailing list. I would say check both of them, but they're unchecked by default. So you'll have to do that by hand. We also have copies of the show at our website, twit.tv slash sn.
[02:49:00] [SPEAKER_00] There's a YouTube channel for the video dedicated to security now. And of course, you can subscribe audio or video and your favorite podcast client. Now, if you want to watch us do it live, it's right after Mac Break Weekly. Every Tuesday, it's supposed to be and usually is close to roundabout somewhere within an hour of 1.30 p.m. Pacific, 4.30 Eastern, 20.30 UTC. You can watch live if you're in the club. And I hope you are because that really helps us out, helps us keep doing these shows.
[02:49:30] [SPEAKER_00] If you're in the club, you can go to the club, Twitter, Discord and watch there with all the other club members. But you can also watch, everybody can, YouTube, Twitch, X.com, Facebook, LinkedIn. And kick, we stream it every month. Thank you, everybody, for joining us. Thank you, Mr. G. Have a wonderful evening. And we'll see you next week. See you on the 29th.
[02:49:51] [SPEAKER_01] Bye.